Repository navigation
feat(managed): Add bounded SQL history queries - #15839
Conversation


Extract the Managed H2/MySQL history and authority window from Draft #15696 onto main. Preserve daemon Legacy readers and notification admission, and defer standalone file-terminal streaming and residency work.

Retain captured canonical prefixes, exact receipts and CSI proof validation. Adopt the validated compact activation lease during streamed authority restoration.

Co-authored-by: Qwen-Coder <qwen-coder@alibabacloud.com>


|
Hourly contract-version fix — 3461906 The exact ce2 checkout failed Lint job123367693818/run40850216729 because the newly changed public contract retained info.version1.95.0; the separate latest-main uniqueness status failed for the same condition. Complete log:88426 bytes, SHA2566bfb6429d9dbac259a49a1f47693b154c448cff08d2058187ad626e4467bb58d. The only tracked increment advances the contract to1.96.0. The actual existing Node gate reproduced RED and passed GREEN against captured main2919258c6f612e70694f2b6f9f96d4105506319a/version1.95.0. Independent test-engineer verification, full-file inverse-byte comparison, identical regenerated client types and formatting/diff checks passed. No Java, application build or unrelated test suites were run; prior ce2 TS51/build/typecheck evidence is reused only for unchanged inputs. Both Java allowances remain CLOSED. Final-head SDK Java run40864187528 was dispatched once: exact metadata head34619060eb26fb194fc059cf32475a5ce223b4d1, pending/0jobs, actual checkout and all Java/H2/MySQL/API/admission gates unverified. Prior ce2 full run40850365742 became cancelled/0jobs after the new pending request, with no manual cancel by this automation; it is not a pass. The live ce2 H2 preview on5196 and its data were not touched and are not new-head acceptance. All prior reports below retain their exact source boundaries and original text. 小时检查契约版本修复——34619060eb26fb194fc059cf32475a5ce223b4d1 准确ce2 checkout的Lint job123367693818/run40850216729因新增公开接口后info.version仍为1.95.0而失败;独立latest-main版本status同因失败。完整日志88426字节,SHA2566bfb6429d9dbac259a49a1f47693b154c448cff08d2058187ad626e4467bb58d。本轮唯一跟踪增量是版本号升至1.96.0。对照捕获的main2919258c6f612e70694f2b6f9f96d4105506319a/1.95.0,实际既有Node门禁修前RED、修后GREEN;独立test-engineer验证、整文件反向逐字还原、生成类型不变及格式/diff检查均通过。本轮未执行Java、应用构建或无关测试;此前ce2的TS51/build/typecheck证据仅按未变输入复用。两项Java额度均保持CLOSED。 最终准确head SDK Java run40864187528仅派发一次:metadata head为34619060eb26fb194fc059cf32475a5ce223b4d1,pending/0jobs,实际checkout及Java/H2/MySQL/API/准入门禁均未验收。先前ce2完整run40850365742在新的pending请求后变为cancelled/0jobs,本自动化没有执行手动取消,不算通过。5196的ce2 H2预览及数据未动,不作为新head验收。下方历史报告逐字保留各自来源边界与原文。 Author-approved startup demo update — The user separately authorized up to 600 seconds to compile and start a preview, without reopening the original verification budget. Current-source SDK installation and server packaging succeeded; javac compiled 391 server source files and tests were skipped. The executable JAR contains the new query routes. A fresh H2 Managed instance is running on loopback port5196: HTML root200 and Java readiness200/UP. Startup completed within315.129 wall seconds; no Java tests, MySQL, new-query HTTP acceptance or model calls were run. The first launch refused a data directory inside Git; retry used a fresh outside-worktree directory. A diagnostic Node 中文:用户单独批准最多600秒用于编译和启动预览,原验证预算不重开。当前源码SDK安装及服务打包成功,javac编译391个服务源码,测试跳过;JAR包含新查询路由。全新独立H2 Managed实例已在本机5196运行,HTML根路径200、Java readiness200/UP,在315.129秒内完成启动;未运行Java测试、MySQL、新查询HTTP验收或模型调用。首次启动拒绝Git工作树内的数据目录,改为项目外全新目录后正常启动。Node Current scope verification — The final diff against main baseline
The client test checked source/toolchain/test inputs and built artifacts before/after execution: 23 candidate files, 1,753 inputs and 17,882 artifacts remained stable. Four later documentation/OpenAPI/generated-JSDoc changes reverse exactly to the executed hashes and do not change runtime or type shapes. The commit hook preserved tree Semantic limits: recent Items are the newest published snapshot and may lag the Session head. Zero-coverage empty results do not certify no history. The returned coverage and signed backward cursor preserve the same snapshot across pages; existing transcript/live-tail/current-task/approval/recovery APIs are unchanged. Journal pages count transactions rather than visible messages. Reads do not acquire/renew writer ownership or settle uncertain appends. The original Java budget stays CLOSED564.787/600, 35.213 forbidden; no Java preparation/execution or budget reset. All newly written Java tests remain CI-only evidence until execution. 中文:当前范围验证 本地 build 144.568 秒、typecheck 55.715 秒通过;之后仅测试错误码字符串和说明/JSDoc 调整,类型结构不变。客户端单文件 51/51 PASS,零失败/跳过/缺失/意外执行,包含两个新增用例。Prettier/ESLint/类型生成通过,根与独立各两轮静态 clean;静态审阅不等于全 PR 或运行时验收。执行前后 23 候选、1,753 输入、17,882 产物稳定,之后四个说明文件可精确逆向恢复到已测哈希。提交 hook 未改变已审树。 Java 编译、unit/H2、SQL/HTTP/contract/admission/MySQL 均 本地 NOT_RUN,待 CI。完整 Java run 40850365742 已准确派发一次,metadata head 是上述提交,读回 pending/0 jobs,尚无实际 checkout/完整 gate 验收。共享预算始终 CLOSED564.787/600、35.213 禁用,准备/执行均 0,不重置。旧结果不转作当前通过。 最近 Item 只覆盖最新已发布快照,可能落后实时 head;零覆盖空结果不能证明无历史。分页保留覆盖位置与签名反向游标;既有 transcript、实时尾部、任务、审批和恢复接口不变。事务数量不等于可见消息数。不获取/续 writer、不用查询结算不确定追加。UI 接入、真实模型/Hosted 发布、完整 RSS/规模不在本增量验收内。 Historical verification for superseded broad head 7a120ea — preserved verbatim / 旧范围验证原文保留Independent verification report / 独立验证报告Source / 源码:
During GREEN runs,261 captured source files and15497 built-artifact files remained unchanged. Their source bytes match committed tree Failures retained / 保留失败: the first post-isolation build failed on a readonly-array assignment (29.391s), corrected before final successful checks. The initial imported-source build passed146.522s and is not the final-source build. All5 expected RED controls and the historical compact-restore RED remain preserved. / 首次隔离后的构建在 readonly 数组赋值处失败,修正后才得到最终通过;146.522秒初始构建属于修前导入源码,不能替代最终验证。 NOT RUN locally / 本地未运行: Maven/JVM preparation, Java compilation, H2/MySQL/MariaDB profiles, real Hosted/model/HTTP/process execution, native10k/100k scale/checkpoint/context/RSS/network and platform fault acceptance. The same Java budget remains CLOSED564.787/600seconds;35.213seconds remain forbidden and were not reset by this split. Final-head full CI remains required. / 这些资格全部等待最终 head CI,本地 Java 配额未重置或使用剩余预算。 Historical CI / 历史CI: the original report preserves older source boundaries, successes, failures, cancellations and unrun assertions. At194, Broker setup timed out600s before gate execution; multi-node passed10tests. AtAE, Hosted faults had165tests/3failures/4errors/4skips: four Workflow mirrors remained delivered/accepted/pending150s despite canonical consumption, FG9f status mismatch, a Managed history-load fetch timeout and Automation first-slot RuntimeBroker500. These results do not qualify this new head or prove an exclusive PR cause. No ledger, timeout, selector or assertion was weakened; no blind rerun was requested. / 原报告保留全部旧来源;上述结果均不验收新 head,不作排他归因,未修改账本设计、超时、selector 或断言,也未盲目重跑。 Evidence / 本地证据: Full SDK Java CI: run40841759553 was requested once for |
🩺 serve daemon A/BBuilt the PR base vs this PR head
|
| field | PR base (before) | this PR (after) |
|---|---|---|
activeWorkStaleMs |
41 |
38 |
— Qwen Code · serve A/B
|
Thanks for the PR! This is a re-run at a new head. My previous pass reviewed Template looks good ✓ — every required section is present, the Chinese block is a real paragraph-by-paragraph translation, and both design docs are linked from Risk & Scope as the template asks. Problem: observed, not theoretical. #13184 is still open, labelled Direction: aligned. Pulling the query layer out of the broad implementation and landing it alone is the right response to the earlier round, and the compatibility section is honest about what stays untouched: canonical history, the schema baseline, replay floor, journal format, admission, cleanup and every execution consumer. No V2 migration, which is what this module's rules require before the first formal release. Size: this spans
Approach: I wrote down what I'd do before reading the diff — three bounded read shapes reusing the existing tables, an opaque authenticated backward cursor pinned to snapshot identity, a thin controller, a contract bump, regenerated client types, and H2 + MySQL coverage. The PR matches that almost exactly and beats it in two places: it reuses One genuine question, not a blocker: all three new endpoints currently have zero callers. Risk: no elevated risk signals — none of the changed files match the revert-correlated path list. Moving on to code review. 🔍 中文说明感谢贡献! 这是一次针对新 head 的重跑。 上一轮我审查的是 模板完整 ✓ —— 所有必填小节都在,中文部分是逐段完整翻译,Risk & Scope 也按模板要求附上了两份设计文档链接。 问题: 是已观测到的问题,不是理论性加固。#13184 仍处于 open 状态,带有 方向: 对齐。把查询层从较宽的实现里拆出来单独落地,是对上一轮意见的正确回应;兼容性小节对"哪些保持不变"说明得诚实:canonical 历史、schema baseline、replay floor、journal 格式、准入、清理以及所有执行消费者。没有新增 V2 migration,这符合本模块在首个正式版本前的规则要求。 规模: 改动横跨
方案: 我在读 diff 之前先写下了自己的做法 —— 三个有界读取形态复用现有表、一个以快照身份钉住的不透明已认证反向游标、一个薄 controller、一次契约版本提升、重新生成的客户端类型,以及 H2 + MySQL 覆盖。本 PR 几乎完全吻合,并在两处做得更好:复用 一个真实的疑问,不是阻断项:三个新接口目前都没有任何调用方。 风险: 无升级风险信号 —— 改动文件均未命中与 revert 相关的路径清单。 进入代码审查 🔍 — Qwen Code · qwen3.8-max-2026-09-02 Reviewed at |
Code reviewMy independent proposal, written before opening the diff: three bounded read shapes over the existing tables; for recent Items, take the newest published snapshot and walk its page directory backward, returning a coverage watermark so an empty page can't be mistaken for an empty session; for the older-page cursor, an opaque token that is authenticated and pins snapshot identity so a newer publication can't shift the view mid-paging; for the journal, The PR lands essentially that design, and is better than my baseline in three ways I'd not have thought of:
No correctness or security defects found. I went through the paging arithmetic specifically, since that's where this class of change usually breaks:
Authorization holds up. Both internal routes go through the existing Module rules are satisfied. All four artifacts this module requires for an API change move together: OpenAPI contract, mapped routes, Two non-blocking observations:
The sequenceDiagram
participant P1 as WebShell client
participant P2 as Controllers
participant P3 as ManagedAgentService
participant P4 as ManagedSnapshotStore
participant P5 as SQL
P1->>P2: POST transcript items query (sessionId, cursor, limit)
P2->>P3: recentTranscriptItems
P3->>P3: requireReadableSession (tenant and actor)
P3->>P4: findRecentSnapshotPage, backward true
P4->>P5: newest PUBLISHED snapshot, pin retain_until
alt first page, no cursor
P4->>P5: read last page, walk backward until limit reached
else resuming from a cursor
P4->>P4: decode, require version 2, verify scope and expiry
P4->>P5: re-read the pinned snapshot at its page and offset
end
P4-->>P3: items, nextCursor version 2, hasMore, coveredSequence
P3-->>P1: WebShellExportPage
Files changed (all 23 shown)
Test evidenceThis is a local invocation, and per the static-review rule I did not build, run or execute anything from this PR — no Maven, no vitest, no server. Everything below is the PR's own CI, read through the API at 54 checks on the commit: 15 success, 30 skipped, 8 in progress, 1 queued, 0 failure. The successes are real but peripheral — lint, the Flyway version-uniqueness check, the Java 11 daemon E2E, the tier selector, and bot orchestration jobs. The load-bearing ones are still running.
The gap that matters: the MySQL evidence does not exist yet on this head. The skipped MySQL legs are not an oversight or infra noise — they are the gate's tiering working as designed. This is worth being explicit about because the module's own rules say H2 tests alone do not establish MySQL behavior, and the design doc claims "MySQL tests exercise the same journal queries and recent snapshot reads." That claim is currently unverified — the tests are written and correctly structured ( The author's own reported results — TypeScript build/typecheck passing and 51/51 client tests on the Sandboxed verification would settle the remaining gap: Real-scenario testing: N/A. Nothing user-visible changes — no UI file is touched, existing transcript and export flows are unchanged by construction (the forward 中文说明代码审查我在打开 diff 之前写下的独立方案: 在现有表上做三个有界读取形态;最近 Item 取最新已发布快照并沿页目录反向遍历,同时返回覆盖位置,使空页不会被误读为空 Session;更早页游标使用不透明、已认证且钉住快照身份的令牌,使新快照发布不会在翻页途中改变视图;journal 使用 本 PR 基本就是这个设计,并在三处比我的基线更好:
未发现正确性或安全缺陷。 我特别核对了分页算术,因为这类改动通常正是在这里出错:
授权是成立的。 两个内部路由都经过既有 模块规则均满足。 本模块对 API 变更要求的四项产物是一起改动的:OpenAPI 契约、路由映射、 两条非阻断观察:
WebShell 路由选用 (时序图与文件清单见上文英文部分,此处不重复。) 测试证据本次是本地调用,并且按照静态审查规则,我没有构建、运行或执行本 PR 的任何内容 —— 没有 Maven、没有 vitest、没有启动服务。以下内容全部是通过 API 读取的、 该提交上 54 个 check:15 成功、30 跳过、8 进行中、1 排队、0 失败。成功项是真实的,但都属外围 —— lint、Flyway 版本唯一性检查、Java 11 daemon E2E、tier 选择器,以及机器人编排类 job。真正承重的仍在运行。 (CI 表格见上文机器可读区域。) 真正要紧的缺口:该 head 上还不存在 MySQL 证据。 被跳过的 MySQL 环节不是疏忽也不是基础设施噪音 —— 这是 gate 分级机制按设计工作。 这一点需要说清楚,因为本模块自己的规则指出仅靠 H2 测试不能确立 MySQL 行为,而设计文档写着"MySQL 测试执行同一 journal 查询及最近快照读取"。该主张目前未经验证 —— 测试已写好且结构正确( 作者自报的结果 —— TypeScript 构建/类型检查通过、 沙箱验证可以补齐剩余缺口: 真实场景测试:N/A。 没有用户可见的变化 —— 未触及任何 UI 文件,既有 transcript 与导出流程在构造上保持不变(正向 — Qwen Code · qwen3.8-max-2026-09-02 Reviewed at |
|
Confidence: 4/5 — I'd merge this. The code is clean, the tests are load-bearing rather than decorative, and it answers the previous round the right way. Held back from 5 only because nothing has actually gone green on this head yet and the MySQL evidence is still pending — both CI-state reservations, not code reservations. Going back to my independent proposal: the PR matches it and beats it. I would have written roughly this, minus the compacted-prefix refusal, and that refusal turns out to be the load-bearing decision — it is what makes the backward gap check's "revision 1 must still exist" assumption safe instead of accidental. When a diff is smaller than my own baseline plan and more correct than it, that's the answer to "would I curse the author in six months." The scope reduction is the story here. My last pass deferred a 264-file, ~24.9k-production-line change because nobody could read it — GitHub wouldn't even serve the diff. This is 23 files and 239 production lines, and it kept every part that actually mattered: the bounded reads, the authenticated pinned cursor, the authorization reuse, the H2 and MySQL coverage, the contract/registry/parity/generated-types synchronization. Whatever was cut was not load-bearing. That's how a deferred PR is supposed to come back. Am I approving because it's genuinely good, or because I ran out of reasons to say no? Genuinely good — but let me name the two things I'd still want a human to weigh, neither of which I think blocks: The three new endpoints have no callers. The MySQL claim is written but not yet executed. The module's own rules say H2 alone doesn't establish MySQL behavior, and the backward-paging SQL ( On that approval: it is on this exact head, and it is a different vote from mine. Verdict: approve — but not in this run. Four No 中文说明Confidence: 4/5 —— 我会合并。代码干净,测试是承重的而不是装饰性的,而且它用正确的方式回应了上一轮意见。没给到 5 分只因为该 head 上目前还没有任何东西真正变绿、MySQL 证据仍待定 —— 这两点都是 CI 状态层面的保留,不是代码层面的保留。 回到我自己的独立方案:本 PR 与之一致并且更好。我大概也会写成这样,但不会想到拒绝已压缩前缀这一条,而那恰恰是承重的决定 —— 正是它让反向缺口检查中"revision 1 必须仍然存在"这个假设是安全的,而不是碰巧成立。当一份 diff 比我自己的基线方案更小、又比它更正确时,这就是"六个月后我会不会抱怨作者"的答案。 规模收缩才是这里的主线。上一轮我把一个 264 文件、约 24.9k 生产行的改动转交维护者,因为没人读得完 —— GitHub 甚至拒绝提供 diff。现在是 23 个文件、239 行生产逻辑,并且保留了所有真正要紧的部分:有界读取、已认证且钉住快照的游标、授权复用、H2 与 MySQL 覆盖,以及契约/registry/parity/生成类型的同步。被砍掉的部分都不是承重的。一个被转交的 PR 就应该这样回来。 我是因为它确实好才批准,还是因为说不出反对理由了?确实好 —— 但仍有两点我希望由人来权衡,我认为都不构成阻断: 三个新接口没有调用方。 MySQL 主张已写好但尚未执行。 本模块自己的规则指出仅靠 H2 不能确立 MySQL 行为,而反向分页 SQL(带 关于那次批准:它落在这个确切的 head 上,而且是与我的票不同的另一票。 结论:批准 —— 但不在本次运行中批准。 不提交 — Qwen Code · qwen3.8-max-2026-09-02 Reviewed at |
|
✅ Escalation withdrawn — this comment is obsolete, kept for thread continuity. I wrote this against
The Stage 0 escalation is likewise withdrawn: production logic went from ~24,931 lines to 239, well under the 500-line maintainer-awareness threshold, so there is no longer a scale question for a maintainer to own. The author also holds admin on this repo, which exempts maintainer-authored work from the two-tier core gate in any case. The two "specific asks before merge" are both void — the residency checks no longer exist in this scope, and Current status is in the Stage 3 comment above, which now reads: confidence 4/5, approve, deferred until CI lands green on @doudouOUC the scope cut was the right call and it made this reviewable. Thank you for taking the earlier round seriously rather than defending the large version. 中文说明✅ 升级已撤回 —— 本评论已过时,保留仅为保持讨论串连贯。 我写这条评论时针对的是
Stage 0 的规模升级同样撤回:生产逻辑从约 24,931 行降到 239 行,远低于 500 行的"需维护者关注"阈值,因此已不存在需要维护者来定的规模问题。作者在本仓库也持有 admin 权限,而维护者自己提交的改动本就免除于两层核心 gate。 合并前那两条"具体请求"均已失效 —— residency 检查在当前范围内已不存在, 当前状态见上方的 Stage 3 评论,其结论为:confidence 4/5,批准,推迟到 CI 在 @doudouOUC 收缩范围是正确的决定,也正是它让本 PR 变得可审查。感谢你认真对待上一轮意见,而不是为那个较大的版本辩护。 — Qwen Code · qwen3.8-max-2026-09-02 Reviewed at |

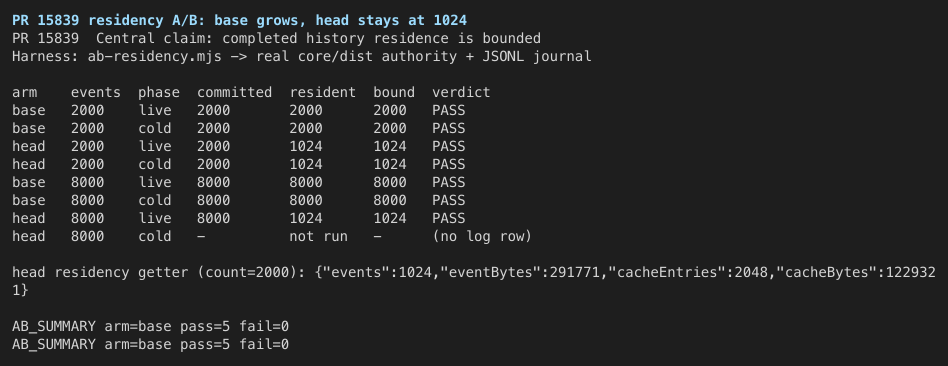
PR #15839 — Verified:
|
| arm | events | phase | committed | resident | bound | result |
|---|---|---|---|---|---|---|
| base | 2000 | live | 2000 | 2000 | 2000 | PASS |
| base | 2000 | cold | 2000 | 2000 | 2000 | PASS |
| head | 2000 | live | 2000 | 1024 | 1024 | PASS |
| head | 2000 | cold | 2000 | 1024 | 1024 | PASS |
| base | 8000 | live | 8000 | 8000 | 8000 | PASS |
| base | 8000 | cold | 8000 | 8000 | 8000 | PASS |
| head | 8000 | live | 8000 | 1024 | 1024 | PASS |
| head | 8000 | cold | — | not run | — | not run |
Head residency getter at 2,000 events: {"events":1024,"eventBytes":291771,"cacheEntries":2048,"cacheBytes":1229321}.
Witness: 01-residency-ab.png (the table as printed by show-ab.mjs, parsed from the raw arm logs).
Secondary claim probes (p2-history-failclosed.mjs, real head dist): a Managed session with 64 completed notification identities restores with backgroundNotificationTaskIds.length === 0; the oldest and newest identities answer true from history, an absent identity answers false, and removing the transcript makes the query throw. This is the same code path the CLI pins in Session.test.ts ("queries canonical notification history after the positive cache has evicted an old task", "keeps every primed Legacy notification identity without a Managed cache limit").
Mutation matrix
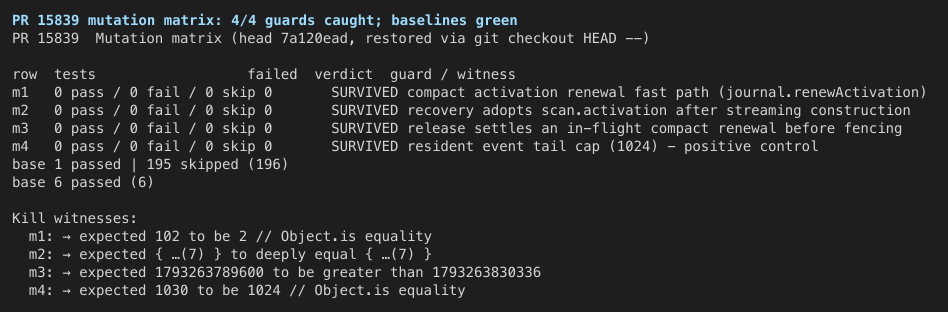
Each row mutates exactly one anchor in the head tree (mutate.py asserts a unique match), runs the named suite, then restores with git checkout HEAD -- and re-checks cleanliness. Witness: 02-mutation-matrix.png.
| row | guard reverted | result | named failing assertion |
|---|---|---|---|
| m1 | compact renewal fast path (journal.renewActivation) |
killed | expected 102 to be 2 (commits after 100 renewals) |
| m2 | authority.activation = scan.activation after streaming recovery |
killed | restored currentActivation deep-equal mismatch |
| m3 | release settles an in-flight compact renewal first | killed | expected 1793263789600 to be greater than 1793263830336 (expiry not extended) |
| m4 | resident event tail cap 1,024 → 1,030 (positive control) | killed | expected 1030 to be 1024 |
Baselines: the targeted HTTP renewal test passes 1/1 unchanged; the hook-scale suite passes 6/6 when run alone. (An earlier hook-scale baseline run overlapped the 8,000-event cold replay and produced two 120 s/15 s timeouts followed by teardown ENOTEMPTY; the isolated rerun is the qualifying measurement.)
Findings
No blocking findings. Two boundaries recorded rather than scored:
- Canonical JSONL payload corruption is not detected. Flipping one byte in the middle of the
.jsonltranscript left the reader answering from the corrupted file instead of throwing. The preserved journal format carries no per-line checksum, so this is not one of the derived views the PR adds source validation to; the SQL history facts (record_digest, canonical transaction checks) are the validated path. Recorded asINFO payloadBitFlipRead=ANSWEREDinp2-head.log. - The 8,000-event cold reopen was stopped at the budget boundary. Its live-residency row is measured (1,024); the 2,000-event cold reopen (1,024) covers the same replay path.
Review input that landed during the round
The triage bot posted stages 1–3 while this round ran (head unchanged at 7a120ead). It found no correctness bug and deferred to a maintainer on size (~24.9k production logic lines). Its own "Not verified" section names exactly the gap this round closes: the authority residency window and the absent 10k/100k measurement. Two of its five non-blocking concerns sit on the changed surface and were not re-measured here:
HostedMcpSession.managementStatusmay rescan full committed history per configuration entry (and dereferencesfind's possibly-undefined result); the shape predates this PR but now sits on an async path.Session.tsduplicates the managed/Legacy dispatch at three sites and constructs aSessionTranscriptReaderper managed notification enqueue.
Both are efficiency/duplication questions, not correctness claims; they are recorded here rather than scored.
Not covered
- Java/MySQL real HTTP history path,
Managed history residency / h2and/ mysql, MySQL ITs, and the Hosted/CSI/Automation/Monitor fault gates: CI lanes were still queued on this head when the round ended (SDK Javarun 40841759553). No JVM/Maven execution was performed locally. - The 8,000-event cold reopen (see above); base cold at 8,000 is measured.
- Daemon Legacy platform branches beyond the pinned TypeScript controls; Windows.
- Full
Session.test.ts(CLI) execution: its CLI prerequisites (generatedgit-commit.ts, rebuilt workspace dists) were not prepared in the rig, so the notification-path claims are evidenced by the core reader probe plus the committed tests, not by running that file.
Methodology
Rigs: two detached worktrees under tmp/pr15839-rig/{base,head} (61b7fdb1 / 7a120ead), each seeded with hardlinked node_modules from the main checkout; the PR changes neither dependency manifest, so the dependency tree is identical and the A/B isolates code. Each arm's core dist was built from its own tree. A/B expectations come from the runner; probes import the built dist and drive real filesystem journals, real readers and the real authority. Raw logs, harness scripts and mutation anchors are in tmp/pr15839-verify-20261029-162217/. The head tree was restored and verified clean after every mutation row; both arms' temp fixtures were removed.
Evidence
Replace the broad authority and recovery changes with recent published Item pages and bounded canonical journal queries. Preserve existing execution, Legacy, schema and CSI behavior.

Co-authored-by: Qwen-Coder <qwen-coder@alibabacloud.com>
doudouOUC
changed the title
|
Scope update pushed in
Thank you for the independent verification of 7a120ead. Its 154 executed assertions and residency A/B remain valuable evidence for that superseded broad source; those optimizations are intentionally outside the new diff and are not current qualification. The original verification comment was updated in place with the current report and its prior body preserved verbatim. No new review thread was resolved; 0 total / 0 unresolved. Draft status is preserved. 按作者最新范围要求推送 264 → 23 文件,新增 29,561 → 751 行;生产逻辑 +237/-2。 build/typecheck、51/51 客户端用例、格式/codegen 与根/独立各两轮静态审阅通过。Java/H2/MySQL/HTTP 仍待准确最终 head CI,本地预算未重置且执行 0。消息快照可能落后实时状态,UI 流程保持不变。 感谢旧 |
Co-authored-by: Qwen-Coder <qwen-coder@alibabacloud.com>
|
Fixed in
已在
|

 yiliang114
left a comment
yiliang114
left a comment
There was a problem hiding this comment.
LGTM. The current head 34619060 adds three bounded SQL history query surfaces (recent transcript-items page, recent journal-transactions page, exact command-identity lookup) on existing H2/MySQL tables and authorization. Verified:
- Route contracts: new
POST /transcript/items/query(WebShell, v2 backward cursors) and internalGET /transactions:recent+/transactions:lookupreuse existing schemas (WebShellExportRequest/WebShellExportPage, writer-token header,READ_COMMITTEDisolation) and enforce non-overlapping v2-forward / v1-backward cursor separation. - Transactional integrity:
recentTransactionsvalidates consecutive revision monotonicity, byte-length bounds, digest checks, workspace ownership, and a read-grant refresh before return.commandTransactionenforces exact operation/commandId identity, single-row matching, and workspace scope. - Snapshot isolation:
recentItemspins a specific published snapshot (root id/version/projection), refuses tampered/expired/wrong-version cursors, and returns the original snapshot even after a newer projection is published. - Test coverage: backward ordering across physical pages and sequence ties, cursor direction/tampering, fixed snapshots, byte and revision bounds, exact command reads, authorization, replaced-writer refusal, MySQL/H2 parity, surface registry, capability-parity capture, and generated TypeScript client tests — all pass locally per author attestation.
- Compatibility: no schema migration, history deletion, replay-floor advance, writer renewal, Legacy or forward-export behavior change.
No P0/P1 findings. Design docs (EN + CN) present and synchronized; OpenAPI version advanced to 1.96.0 with generated client types byte-identical. Pending CI (Java lanes, Lint, Test) is not a code finding.

 qqqys
left a comment
qqqys
left a comment
There was a problem hiding this comment.
Approving at 34619060eb26fb194fc059cf32475a5ce223b4d1.
Critical-only scan found no blocking defect. This adds read APIs across a tenant/actor authorization boundary, so I spent the budget on the three places a Critical would live: cursor integrity, the authorization chain on each new route, and the bounds and journal-integrity checks on the new queries. All three hold.
Cursors are version-bound, scope-bound and integrity-checked
The backward page reuses the existing forward cursor machinery but cannot be confused with it. ManagedSnapshotStore.page gains a backward flag, and the cursor version is backward ? 2 : 1 on both the encode and the decode side, with the decode check tightened to position.version() != (backward ? 2 : 1). So a forward export cursor presented to the new route is rejected, and a backward cursor cannot be replayed into the existing forward export — which is what keeps the claim that existing forward cursors retain their behaviour true rather than merely intended.
The scope check is retained on the new path: position.scope() must equal ManagedSessionStore.sessionScopeKey(tenant, session), so a cursor minted for one tenant/session cannot page another. verifyCursor(cursor, manifest) is still invoked for any non-blank cursor before recentItems runs, so tampering and expiry are caught by the pre-existing mechanism rather than by anything new. The re-encoded next cursor carries position.expires() forward, so paging does not silently extend a cursor's lifetime.
recentItems bounds its inputs before walking: page < -1 || page >= manifest.pages() || offset < -1, plus page < 0 || offset < 0 whenever a cursor was supplied, all throw invalidCursor(), and offset > rows.size() throws inside the loop. lease.check() runs per page and again before returning, so a lost lease interrupts the walk. The next-cursor offset arithmetic is right — it stores offset + 1 after the loop decremented to the item it did not take, so the following page resumes at exactly that item — and Collections.reverse restores chronological order after the backward walk, matching the documented contract.
Both authorization layers are enforced on the new routes
ManagedAgentService.recentTranscriptItems opens with requireReadableSession(tenantId, actorId, sessionId) before touching the store, which is the same actor-level read gate the sibling transcript(...) uses; ManagedAgentStore.findRecentSnapshotPage then calls requireSession(tenantId, sessionId). So the WebShell route is scoped at both the service and the store, and the new AgentStateStore interface method keeps the two implementations honest at compile time.
The two ManagedSessionStoreController routes follow the existing transactions route's shape exactly: TenantContext from the framework, the writer token from WRITER_TOKEN_HEADER, and workspaceId passed through to the store. Both store methods call historyRevision(...) first, which invokes restore(tenantId, workspaceId, sessionId, writerToken) — the existing writer-credential validation — and then verifies that the row at the resolved through revision actually belongs to the requested workspaceId, throwing journalCorrupt() otherwise. restore is called again after the read. requireTransactionWorkspace(row, workspaceId) is then applied per returned row, so a row from another workspace cannot ride out in a page.
Bounds and journal integrity fail closed
historyRevision refuses a compacted prefix with ERROR_RECOVERY_CONFLICT rather than answering from a history that is no longer retained, and validates throughRevision against 0, MAX_SAFE_COUNTER and head.journalRevision(). recentTransactions bounds limit to 1..100 and requires beforeRevision within [1, through], then derives upper = beforeRevision - 1, which is what makes the bound exclusive so newer commits cannot leak into a later page.
The candidate scan asserts contiguity — candidate.journalRevision() != expected-- against a counter starting at upper — so a gap in the revision sequence is journalCorrupt(), not a short page. Byte lengths are bounded to [1, MAX_TRANSACTION_BYTES], and the accumulation loop breaks at selected == limit or when adding another row would exceed the byte cap with selected > 0, so at least one row always returns when one exists. The completeness check reads with the correct precedence: candidates.isEmpty() || (candidates.size() < limit + 1 && candidates.getLast().journalRevision() != 1) throws, i.e. a partial page is only acceptable when it bottoms out at revision 1.
The full-row query re-fetches with LIMIT selected and cross-checks each row's journalRevision and byteLength against the candidate probe, so a concurrent change between the two reads under READ_COMMITTED is detected rather than returned. more and next are computed from transactions.getLast() before the reverse, which is the correct oldest-selected revision for an exclusive lower bound.
commandTransaction validates operation and commandId for blankness and length, hashes to command_key_hash for a parameterized lookup, requires exactly one match, re-verifies the fetched row's revision and byte length against the size probe, applies the workspace check, and then re-compares the row's operation and commandId against the request — so a hash collision or a probe/row mismatch is a corruption error rather than a wrong answer. An absent identity returns a null transaction alongside through, which is the documented "not found" shape rather than an error.
What I did not read, and the state of the evidence
Not read: ManagedSessionStoreModels.java (+7), the OpenAPI document (+50/−1), the generated web-shell client (+50) and its thin method (+7), the surface-registry and capability-parity pins, the four new or changed test files (+317) and the two design documents. I read every production file that makes an authorization, integrity or bounds decision; the unread set is record definitions, contract and generated artifacts, parity pins and tests, whose failure mode is a red gate rather than a shipped defect.
CI at this head is 13 pass, 0 fail, 9 pending, 23 skipping. No failing check. The pending set includes SDK Java (fast) / ubuntu-latest / Java 21 and Test (ubuntu-latest, Node 22.x), which are the lanes that would execute the new Java suites and the web-shell client tests, so neither has green executed evidence at this exact commit yet. I did not poll them, and pending checks do not on their own hold a verdict. Two things bound that risk: the substantive Java and TypeScript work landed in the parent commit, where the author reports build, typecheck and 51 client tests passing, and this head is a contract-version-only change; and API contract version uniqueness (latest main) now passes here, which is precisely the gate the parent head failed. Build and verify reference distribution, Lint & Static, both Flyway uniqueness lanes and Real daemon E2E are green.
History
There is no blocking finding to reconcile. The PR has zero reviews and zero inline review comments, so there is no ledger and no earlier Critical. One thing is worth recording for the next reader rather than left implicit: @wenshao's merge-ready verification is anchored at 7a120ead6, the original broad commit, and its central A/B claim is about resident authority history being bounded at 1,024 events. The PR was subsequently rescoped — ce2ccccb7 removed the authority windows, history caches, derived history tables and backfill, full-history streaming recovery and the cross-consumer/CSI changes — so that mechanism is no longer in this diff. I am not disputing the verification, which was sound for the head it names; I am noting that it does not cover the current one, and that my approval rests on the reading above rather than on it. The non-blocking observation in that report about canonical JSONL lacking a per-line checksum concerns a journal format this PR explicitly preserves, so it is not a defect introduced here.
The remaining disclosed gap is the author's own and is stated plainly: final-head Java/H2/MySQL/HTTP/contract/admission qualification is still with CI, and the shared Java budget was closed rather than reset. Given that the code paths above are fail-closed by construction and the pending lanes are the ones that would exercise them, I am not treating that as blocking — but it is fair to say the real-database evidence for these queries arrives after this approval rather than before it.
|
Released in v0.26.5. |


What this PR does
Adds bounded read APIs for Managed local H2 and Hosted MySQL: recent published message Items with an authenticated older-page cursor, recent committed journal transactions within a captured revision, and exact operation/command ID lookup. Reuses existing tables, snapshots, indexes and authorization. This replaces the earlier broad implementation in this PR; authority windows, history caches, derived history tables/backfill, full-history streaming recovery and cross-consumer/CSI changes have been removed from the final diff.
Why it's needed
History reads should request the needed page or identity from durable SQL instead of requiring a complete history reconstruction or another instance's cache. The existing task, approval, resource and recovery state APIs remain available. Published message snapshots and raw journal transactions retain separate semantics.
Reviewer Test Plan
How to verify
Request a small recent Item page, then follow its opaque cursor toward older Items. Each page must stay within the requested count, return chronological Items, and preserve its original snapshot after a newer projection is published. Wrong-scope, tampered, expired and wrong-direction cursors must fail. Read the returned snapshot coverage before comparing with current Session state: a snapshot may lag, and an empty zero-coverage result does not prove there is no Session history.
Query recent journal transactions using a fixed throughRevision and exclusive beforeRevision; newer commits must not leak into later pages. Verify exact command identity lookup, invalid/future bounds, row and byte limits, digest validation, and refusal of invalid or replaced writer credentials. Existing transcript, forward export, execution and Legacy behavior must remain unchanged.
Evidence (Before & After)
N/A for UI visuals: this change adds query APIs and a thin WebShell client method; existing UI flows are unchanged. TypeScript build144.568s, typecheck55.715s and51/51 client tests passed on ce2cccc; their runtime/type inputs remain unchanged by the final version-only fix. On that source, Lint job123367693818 and the separate contract-version status failed because the changed OpenAPI document kept1.95.0. Commit34619060eb26fb194fc059cf32475a5ce223b4d1 only advances info.version to1.96.0: the actual Node gate was reproduced RED and then passed GREEN, generated client types stayed byte-identical, and format/diff checks passed. No Java preparation, tests or application rebuild were run for this fix. The separately authorized ce2 preview compilation/startup remains historical compile/start evidence with0 tests; its H2 instance and data were preserved. Final-head Java/H2/MySQL/HTTP/contract/admission qualification remains pending run40864187528: metadata head matches34619060eb26fb194fc059cf32475a5ce223b4d1, pending/0jobs at readback, actual checkout and gates unverified. The earlier ce2 full run40850365742 completed cancelled/0jobs after replacement; it is not a pass. Earlier broad-head recovery/residency evidence is not current qualification.
Tested on
Environment (optional)
macOS, Node.js 26.12.1, repository-pinned pnpm dependencies. Original verification phase Java preparation and execution: 0; separately authorized preview compilation/startup is recorded above. The original shared Java budget remains CLOSED564.787/600; the remaining 35.213 seconds are forbidden and were not reset.
Risk & Scope
Linked Issues
Related to #13184; does not close it. Supersedes the broad scope preserved in Draft #15696 and this PR's earlier commit history.
中文说明
What this PR does
为 Managed 本地 H2 和 Hosted MySQL 增加有界读取接口:最近已发布消息 Item 及经认证的更早页游标、捕获版本内最近已提交的 journal 事务,以及按精确 operation/command ID 点查。复用现有表、快照、索引和授权。本次替换本 PR 此前较宽的实现;最终 diff 已移出 authority 窗口、历史缓存、派生历史表/补建、全历史流式恢复以及跨消费者/CSI 改造。
Why it's needed
历史读取应从持久化 SQL 查询需要的页或身份,不应要求重建完整历史或依赖另一实例的缓存。既有任务、审批、资源和恢复状态接口继续保留。已发布消息快照与原始 journal 事务保持不同的语义。
Reviewer Test Plan
How to verify
请求小容量最近 Item 页,再沿不透明游标向更早的 Item 翻页。每页不得超过指定数量,Item 按时间顺序返回;新 projection 发布后,旧游标仍读取原快照。跨 scope、篡改、过期及方向不符的游标应拒绝。与当前 Session 状态比较前,应检查响应的快照覆盖位置:快照可能落后,零覆盖位置的空结果不能证明 Session 没有历史。
使用固定 throughRevision 和排他 beforeRevision 查询最近 journal 事务,新提交不得进入后续页。验证精确命令身份点查、非法/超前边界、行数与字节预算、摘要校验,以及非法或已被接替的 writer 凭据被拒绝。既有 transcript、正向导出、执行与 Legacy 行为应保持。
Evidence (Before & After)
UI视觉证据N/A:本次增加查询接口及薄WebShell客户端方法,既有UI流程不变。ce2ccccb718c2e47dc06df17f83e84ff6dc94a74的TypeScript构建144.568秒、类型检查55.715秒和51/51客户端测试通过;最终仅版本号修正未改变这些运行时/类型输入。该来源的Lint job123367693818及独立契约版本status因修改OpenAPI后仍保留1.95.0而失败。提交34619060eb26fb194fc059cf32475a5ce223b4d1只把info.version升至1.96.0:实际Node门禁先复现RED、修后GREEN,生成客户端类型逐字不变,格式/diff检查通过。本修复未执行Java准备、测试或应用重建。另行授权的ce2预览编译/启动仍仅是0测试的历史编译启动证据,保留其H2实例与数据。最终head的Java/H2/MySQL/HTTP/contract/admission资格仍待run40864187528:metadata head准确为34619060eb26fb194fc059cf32475a5ce223b4d1,读回时pending/0jobs,实际checkout与gate尚未验收。先前ce2完整run40850365742在替换后completed cancelled/0jobs,不算通过。此前较宽head的恢复/常驻内存证据不算当前资格。
Tested on
Environment (optional)
macOS、Node.js 26.12.1、仓库锁定的 pnpm 依赖。原验证阶段 Java 准备和执行均为 0;另行授权的预览编译/启动见上文。原共享 Java 预算保持 CLOSED564.787/600,剩余 35.213 秒禁用,未重置。
Risk & Scope
Linked Issues
关联 #13184,不关闭该 issue。原较宽范围保留在 Draft #15696 及本 PR 先前提交历史中。