Skip to content

fix(ci): use live review bot for manual re-review - #17848

Open
yiliang114 wants to merge 1 commit into
mainfrom
fix/16832-live-review-bot
Open

yiliang114 wants to merge 1 commit into
mainfrom
fix/16832-live-review-bot

Conversation

@yiliang114

Copy link
Copy Markdown
Collaborator

What this PR does

Switches the manual review_requested lane in qwen-code-pr-review.yml from the deleted qwen-code-ci-bot account to the live qwen-code-review-bot account, and updates the workflow meta-test fixtures to the same identity. The three job gates and the review-config bot_login output now agree on the account that actually receives review requests and posts PR reviews.

This is intentionally scoped to the manual re-review channel. Other workflows still reference qwen-code-ci-bot and are deliberately left alone here: qwen-autofix.yml (REVIEW_BOT and review-event routing), qwen-autofix-fork-bridge.yml, qwen-autofix-fork-signal.yml, qwen-pr-safety-precheck.yml (manual-precheck comment ownership), and pr-force-push-reminder.yml (automation exclusion). Those are separate consumers or are masked by the collaborator association branches, so changing them would broaden this PR beyond #16832. The RELEASE_SYNC_ACTOR fallbacks in ci.yml and sdk-python.yml are also unchanged because release sync likely uses a different actor identity and I found no evidence that qwen-code-review-bot is its replacement.

Why it's needed

Requesting qwen-code-ci-bot as a reviewer is not usable: GET /users/qwen-code-ci-bot returns 404, and requesting it on an owned PR returned HTTP 422 (Reviews may only be requested from collaborators). Requesting qwen-code-review-bot on the same owned PR was accepted, and the account is a live collaborator (GET /users/qwen-code-review-bot resolves as a User; the collaborator check returns 204). Recent PR reviews in this repository are authored by qwen-code-review-bot; there is no GitHub App identity involved in the observed review author.

The old gate still produced an event run but made every job skip. On PR #17841, requesting qwen-code-review-bot generated pull_request_target run 44522592919, and all review jobs reported skipped because the workflow compared the live request with the dead login.

Reviewer Test Plan

How to verify

  1. Confirm the identity evidence above: old account 404 / reviewer request 422; new account resolves, is a collaborator, is requestable as a reviewer, and is the observed PR review author.
  2. Confirm .github/workflows/qwen-code-pr-review.yml has no qwen-code-ci-bot references and that precheck-pr, review-config, authorize, and the bot_login output all use qwen-code-review-bot.
  3. Run npx vitest run --config ./scripts/tests/vitest.config.ts scripts/tests/qwen-pr-review-workflow.test.js.
  4. Run grep -R ".github/workflows/qwen-code-pr-review.yml" scripts/tests/ and check the dependent suites listed below.
  5. After merge, on an owned open PR only, request qwen-code-review-bot as a reviewer and confirm the 🧐 Qwen Pull Request Review run's jobs start instead of all reporting skipped. This live path cannot be proven before merge because pull_request_target reads the workflow from the base branch.

Evidence (Before & After)

N/A — this is a CI/workflow change with no CLI, TUI, Web UI, or Web Shell surface. The discriminating evidence is the GitHub API/workflow behavior above plus the workflow meta-tests.

Tested on

OS Status
🍏 macOS ✅
🪟 Windows ⚠️
🐧 Linux ⚠️

Environment (optional)

macOS arm64, Node 22.23.4, Vitest 3.2.7. The workflow behavior was reproduced through the GitHub REST API on owned PR #17841 only; the successfully added reviewer was removed afterward.

Risk & Scope

  • Main risk or tradeoff: the actual fixed live trigger can only be observed after this base-branch workflow merges; pre-merge verification is necessarily static and meta-test based.
  • Not validated / out of scope: no full local workflow execution, and the Windows/Linux suites were not run locally. actionlint is available at 1.7.7 but is unusable as a signal on this existing workflow: the full invocation exceeded 120 seconds while invoking ShellCheck, and -shellcheck= then rejected the pre-existing deployment: false environment key as a schema error. The changed workflow is parsed and exercised by the meta-tests.
  • Breaking changes / migration notes: the stale qwen-code-ci-bot repository collaborator entry still needs admin cleanup outside this PR. This PR does not touch the auxiliary consumers listed above or the release-sync actor fallback.

Verification run on commit de64fd1ac96cc6f72be73e0d29f5ba180ab64fb8 (base 933497af52d24d77aceea5c01c1eb4ad6fb400e1):

  • npx vitest run --config ./scripts/tests/vitest.config.ts scripts/tests/qwen-pr-review-workflow.test.js — passed: 282 tests, 3 skipped.
  • grep -R ".github/workflows/qwen-code-pr-review.yml" scripts/tests/ found the dependent suites; qwen-resolve-workflow.test.js passed in the dependent-suite invocation.
  • qwen-triage-workflow.test.js — passed: 216 tests, 11 skipped.
  • review-artifact-upload.test.js — passed: 19 tests.
  • review-worktree-cleanup-workflow.test.js — passed: 24 tests.
  • qwen-autofix-workflow.test.js — the candidate suite had 354 passing tests and three failures; the two checkout-attributable failures passed when rerun after adding the missing sparse-checkout fixtures. The remaining attributes deletions, empty files, renames and octopus merges correctly test hits its explicit 120-second timeout both in this branch and on the clean baseline checkout, so it is a pre-existing local-host timeout, not evidence from this diff.
  • npx prettier --check .github/workflows/qwen-code-pr-review.yml scripts/tests/qwen-pr-review-workflow.test.js — passed.
  • git diff --check — passed.
  • Local wide review: two read-only reviewer passes over the frozen diff reported no correctness or security findings. This is self-review evidence because the changes were authored for this task.
  • qwen review run --effort low --json --timeout-minutes 20 — review-gate unverified: the single attempt produced no verdict before it was stopped; per the issue queue instruction it was not retried.

Linked Issues

Fixes #16832

中文说明

这个 PR 做了什么

把 qwen-code-pr-review.yml 里手动 review_requested 通道从已删除的 qwen-code-ci-bot 账号切换到当前仍在使用的 qwen-code-review-bot 账号,并把对应的 workflow meta-test fixture 更新为同一个身份。三个 job gate 和 review-config 的 bot_login 输出现在都指向实际接收 review 请求并发布 PR review 的账号。

本次改动刻意限定在手动 re-review 通道。其他仍然引用 qwen-code-ci-bot 的 workflow 刻意不在本 PR 修改:qwen-autofix.yml(REVIEW_BOT 和 review 事件路由)、qwen-autofix-fork-bridge.yml、qwen-autofix-fork-signal.yml、qwen-pr-safety-precheck.yml(manual precheck 评论归属)以及 pr-force-push-reminder.yml(自动化排除列表)。这些是独立消费者,或者被 collaborator association 分支掩盖;修改它们会把本 PR 扩大到 #16832 之外。ci.yml 和 sdk-python.yml 里的 RELEASE_SYNC_ACTOR fallback 也未修改,因为 release sync 很可能使用另一个 actor 身份,而且我没有找到能证明 qwen-code-review-bot 就是其替代身份的证据。

为什么需要

请求 qwen-code-ci-bot 作为 reviewer 已经不可用:GET /users/qwen-code-ci-bot 返回 404,并且在我自己的 PR 上请求它返回 HTTP 422(Reviews may only be requested from collaborators)。在同一个自有 PR 上请求 qwen-code-review-bot 成功,该账号也是有效 collaborator(GET /users/qwen-code-review-bot 返回 User;collaborator 检查返回 204)。本仓库最近的 PR review 由 qwen-code-review-bot 发布;观察到的 review 作者不是 GitHub App 身份。

旧 gate 仍会创建事件 run,但会让所有 job 跳过。在 PR #17841 上请求 qwen-code-review-bot 触发了 pull_request_target run 44522592919,所有 review job 都报告 skipped,因为 workflow 拿有效请求和已失效的 login 比较。

Reviewer Test Plan

如何验证

  1. 核对上面的身份证据:旧账号 404 / reviewer 请求 422;新账号存在、是 collaborator、可以被请求为 reviewer,并且就是观察到的 PR review 作者。
  2. 确认 .github/workflows/qwen-code-pr-review.yml 不再有 qwen-code-ci-bot 引用,并且 precheck-pr、review-config、authorize 和 bot_login 输出都使用 qwen-code-review-bot。
  3. 运行 npx vitest run --config ./scripts/tests/vitest.config.ts scripts/tests/qwen-pr-review-workflow.test.js。
  4. 运行 grep -R ".github/workflows/qwen-code-pr-review.yml" scripts/tests/,并检查下面列出的相关套件。
  5. 合并后,只能在自有且打开的 PR 上请求 qwen-code-review-bot 作为 reviewer,并确认 🧐 Qwen Pull Request Review run 的 job 会启动,而不是全部报告 skipped。合并前无法证明这条 live path,因为 pull_request_target 会读取 base branch 上的 workflow。

Before / After 证据

N/A —— 这是 CI/workflow 改动,没有 CLI、TUI、Web UI 或 Web Shell 用户界面。可判别证据是上面的 GitHub API/workflow 行为以及 workflow meta-test。

已测试平台

OS 状态
🍏 macOS ✅
🪟 Windows ⚠️
🐧 Linux ⚠️

环境(可选)

macOS arm64,Node 22.23.4,Vitest 3.2.7。Workflow 行为只在我自己的 PR #17841 上通过 GitHub REST API 复现;成功添加的 reviewer 随后已移除。

风险与范围

  • 主要风险或取舍:修复后的真实 live trigger 只能在 base-branch workflow 合并后观察;合并前验证必然只能是静态检查和 meta-test。
  • 未验证 / 不在范围内:没有执行完整本地 workflow,也没有在本地跑 Windows/Linux 套件。本机有 actionlint 1.7.7,但它对这个既有 workflow 无法提供有效信号:完整调用在调用 ShellCheck 时超过 120 秒,-shellcheck= 后又把既有的 deployment: false environment key 报成 schema 错误。变更后的 workflow 由 meta-test 完成解析和覆盖。
  • Breaking changes / migration notes:仓库 collaborator 列表里过期的 qwen-code-ci-bot 条目仍需要管理员在 PR 外清理。本 PR 不修改上面列出的辅助消费者,也不修改 release-sync actor fallback。

在提交 de64fd1ac96cc6f72be73e0d29f5ba180ab64fb8(base 933497af52d24d77aceea5c01c1eb4ad6fb400e1)上完成以下验证:

  • npx vitest run --config ./scripts/tests/vitest.config.ts scripts/tests/qwen-pr-review-workflow.test.js —— 通过:282 个测试,3 个跳过。
  • grep -R ".github/workflows/qwen-code-pr-review.yml" scripts/tests/ 找到了相关套件;qwen-resolve-workflow.test.js 在相关套件调用中通过。
  • qwen-triage-workflow.test.js —— 通过:216 个测试,11 个跳过。
  • review-artifact-upload.test.js —— 通过:19 个测试。
  • review-worktree-cleanup-workflow.test.js —— 通过:24 个测试。
  • qwen-autofix-workflow.test.js —— 候选分支套件有 354 个测试通过、3 个失败;其中两个由 sparse checkout 缺少 fixture 导致的失败,在补齐 fixture 后单独重跑通过。剩下的 attributes deletions, empty files, renames and octopus merges correctly 在本分支和干净 baseline checkout 都会触发显式 120 秒超时,因此这是本机既有的超时问题,不是本次 diff 的证据。
  • npx prettier --check .github/workflows/qwen-code-pr-review.yml scripts/tests/qwen-pr-review-workflow.test.js —— 通过。
  • git diff --check —— 通过。
  • 本地 wide review:两个只读 reviewer 对冻结 diff 分别检查 correctness 和 security,均未发现问题。由于本任务由我完成实现,这属于 self-review 证据。
  • qwen review run --effort low --json --timeout-minutes 20 —— review-gate 未验证:单次尝试没有返回 verdict,已被停止;按 issue queue 指示没有重试。

Linked Issues

Fixes #16832

@github-actions github-actions Bot added the review/self-reported The linked issue was opened by the PR author (self-reported) label Nov 19, 2026
@qwen-code-review-bot

qwen-code-review-bot commented Nov 19, 2026 •

Copy link
Copy Markdown
Collaborator

⚠️ Deferred approval withheld — 1 PR CI workflow run(s) on de64fd1 did not finish green; see the updated table in the Stage 2 comment. Re-run @qwen-code /triage after fixes. finalize run

⚠️ 延迟审批已搁置 —— de64fd1 有 1 个 PR CI workflow 未以绿色完成,详见 Stage 2 评论中已更新的表格。修复后可重新运行 @qwen-code /triage。查看 finalize 运行

@qwen-code-review-bot

Copy link
Copy Markdown
Collaborator

Thanks for the PR!

Template looks good ✓ — all required headings present, including the bilingual summary.

Problem: this is an observed bug, not theoretical hardening, and I re-verified the core evidence independently via the API rather than taking the description's word for it:

Direction: aligned. This is internal CI maintenance that keeps the manual re-review channel functional — squarely within the repo's developer-tooling mission. No direct CHANGELOG reference for a bot-identity switch (the re-review entries there are about review logic, not which account receives requests), but the area is relevant.

Size: not applicable — no core paths touched. Two files, +25/−15: one workflow and its meta-test.

Approach: the scope feels right. It is a minimal identity swap — three review_requested gates plus the review-config bot_login output, with the test fixtures moved to the same identity. You deliberately left the other qwen-code-ci-bot consumers (qwen-autofix*, qwen-pr-safety-precheck, pr-force-push-reminder, the RELEASE_SYNC_ACTOR fallbacks) alone and explained why; that keeps this focused on #16832 instead of broadening into a repo-wide rename. No drive-by refactors or unrelated edits in the diff.

Risk: no elevated risk signals — none of the changed paths match the high-risk revert-correlated set.

Moving on to code review. 🔍

中文说明

感谢贡献!

模板完整 ✓ —— 所有必需标题齐全,含中文说明。

问题:这是已观测到的 bug,而非理论性加固。我通过 API 独立复核了核心证据,而非只采信描述:

方向:对齐。这是保持手动 re-review 通道可用的内部 CI 维护,属于仓库开发者工具使命范畴。CHANGELOG 没有关于 bot 身份切换的直接条目(那里的 re-review 条目讲的是 review 逻辑,而非哪个账号接收请求),但领域相关。

规模:不适用 —— 未触及核心路径。两个文件,+25/−15:一个 workflow 及其 meta-test。

方案:范围合理。这是一次最小化的身份替换——三个 review_requested gate 加上 review-config 的 bot_login 输出,测试 fixture 同步到同一身份。你刻意保留了其他 qwen-code-ci-bot 消费者(qwen-autofix*、qwen-pr-safety-precheck、pr-force-push-reminder、RELEASE_SYNC_ACTOR fallback)并说明了原因,使本 PR 聚焦 #16832,而非扩大成全仓库改名。diff 中没有顺手重构或无关改动。

风险:无升级风险信号——改动路径均不匹配高 revert 相关的高风险集合。

进入代码审查 🔍

— Qwen Code · qwen4-max

Reviewed at de64fd1ac96cc6f72be73e0d29f5ba180ab64fb8 · re-run with @qwen-code /triage

@qwen-code-review-bot

qwen-code-review-bot commented Nov 19, 2026 •

Copy link
Copy Markdown
Collaborator

Code review. My independent baseline before reading the diff: the manual lane dies because three job gates and the review-config bot_login constant compare requested_reviewer.login against a deleted account, so the fix is to point those four sites at the live account that actually receives review requests and posts reviews — and move the meta-test fixtures with them. The diff matches that exactly, and I checked the consistency rather than assuming it:

  • At the head commit, qwen-code-pr-review.yml has zero qwen-code-ci-bot references. The three gates (precheck-pr L106, review-config L236, review-pr L342) and the bot_login output (L245) all read qwen-code-review-bot, and the explicit-trigger branch at L502 derives from needs.review-config.outputs.bot_login, so the sites cannot desync. The other bot_login occurrences in the file are runtime gh api user credential lookups, unrelated to the constant.
  • The head meta-test file also has zero qwen-code-ci-bot left. Crucially, botLogin is parsed from the workflow (review-config → Set review constants → bot_login=([A-Za-z0-9-]+)), so expect(botLogin).toBe('qwen-code-review-bot') genuinely pins the change — it would fail if the workflow still named the old account. This is not a fixture that passes regardless of the diff.
  • Per the AGENTS.md workflow-meta-test rule, I checked the other suites that parse this workflow: qwen-resolve-workflow.test.js makes no bot-login / requested_reviewer assertion, and qwen-triage-workflow.test.js only pins the autofix bot (qwen-code-dev-bot), not the review bot. The remaining ci-bot references in scripts/tests all belong to the other workflows that are legitimately out of scope. So no dependent suite is left asserting the old identity against this file.

No critical blockers and no AGENTS.md violations. The change is minimal, internally consistent, and the test pins it. (Small focused PR — no sequence diagram or files table needed.)

Test evidence — the PR's own CI, read via the API (I did not run any PR code). Snapshot at the reviewed commit; no failures so far. Lint & Static, Build unit-test tree (Linux), and Managed Agent gate are green. The Linux unit suites — which execute the workflow meta-tests, including the changed qwen-pr-review-workflow.test.js — are still running, as are the integration / web-shell / TUI-parity suites. The 36 skipped checks are the review-lane jobs (not triggered by a pull_request event), the macOS/Windows suites, and the sandboxed verify/tmux lanes; their skipping is expected here, not a signal. Because the unit suites are still in flight, I am not claiming the meta-tests pass on CI yet — the table below is a live snapshot and the finalize job will rewrite it once CI settles.

Final CI results for de64fd1 (auto-updated by the triage finalize job after CI completed):

Check Conclusion
Linux unit tests (shard 1/2) ❌ failure
Test (ubuntu-latest, Node 22.x) ❌ failure
Build unit-test tree (Linux, Node 22.x) ✅ success
Check TUI impact ✅ success
Classify PR ✅ success
Integration Tests (no-AK, No Sandbox) ✅ success
Integration Tests (no-AK, shard 1/2) ✅ success
Integration Tests (no-AK, shard 2/2) ✅ success
Lint & Static (ubuntu-latest, Node 22.x) ✅ success
Linux unit tests (shard 2/2) ✅ success
Managed Agent gate ✅ success
Select the Managed Agent tier ✅ success
TUI parity snapshots (ink vs opentui) ✅ success
web-shell E2E Smoke (shard 1/2) ✅ success
web-shell E2E Smoke (shard 2/2) ✅ success
web-shell E2E Smoke (ubuntu-latest, Node 22.x) ✅ success

One row per check name (latest run); skipped checks omitted; failures sort first. / 每个检查名一行(取最新一次运行),省略 skipped,失败项排在最前。

Sandboxed lane (2b-bis) — explicitly not applicable here. The central claim is a GitHub Actions event-gate ("requesting the live bot now starts the review jobs instead of all skipping"), not product runtime behavior. @qwen-code /verify and @qwen-code /tmux drive the CLI product and cannot exercise a base-branch pull_request_target reviewer-request gate, so naming them would be noise. What does substantiate the change is the meta-test that parses the gate (above) plus the API identity facts I independently re-verified in Stage 1. The residual live end-to-end trigger is inherently post-merge-only — pull_request_target reads the workflow from the base branch — and the author flags this honestly; it is not a gap a pre-merge lane can close.

Real-scenario testing (2c): N/A. Unattended CI run, and this is a CI/workflow change with no CLI, TUI, Web UI, or Web Shell surface — nothing user-visible to drive.

中文说明

代码审查。 读 diff 前我的独立判断:手动通道失效,是因为三个 job gate 和 review-config 的 bot_login 常量把 requested_reviewer.login 与一个已删除账号比较;修法就是把这四处指向实际接收 review 请求并发布 review 的有效账号,并同步移动 meta-test fixture。diff 与此完全一致,我核对了一致性而非想当然:

  • head commit 上,qwen-code-pr-review.yml 已无任何 qwen-code-ci-bot 引用。三个 gate(precheck-pr L106、review-config L236、review-pr L342)与 bot_login 输出(L245)均为 qwen-code-review-bot,L502 的显式触发分支从 needs.review-config.outputs.bot_login 派生,因此各处不会脱节。文件中其余 bot_login 是运行时 gh api user 凭据查询,与该常量无关。
  • head meta-test 文件也无残留 qwen-code-ci-bot。关键在于 botLogin 是从 workflow 解析的(review-config → Set review constants → bot_login=([A-Za-z0-9-]+)),所以 expect(botLogin).toBe('qwen-code-review-bot') 真正钉住了改动——若 workflow 仍写旧账号,该用例会失败。这不是无论 diff 如何都通过的 fixture。
  • 按 AGENTS.md 的 workflow meta-test 规则,我检查了其他解析该 workflow 的套件:qwen-resolve-workflow.test.js 不做 bot-login / requested_reviewer 断言;qwen-triage-workflow.test.js 只钉 autofix bot(qwen-code-dev-bot),而非 review bot。scripts/tests 中其余 ci-bot 引用都属于合理不在本次范围内的其他 workflow。因此没有依赖套件仍对该文件断言旧身份。

无关键阻塞项,无 AGENTS.md 违规。改动最小、内部一致,且测试钉住了它。(小型聚焦 PR——无需时序图或文件表。)

测试证据——通过 API 读取 PR 自身 CI(我未运行任何 PR 代码)。 所审 commit 的快照;目前无失败。Lint & Static、Build unit-test tree (Linux)、Managed Agent gate 已绿。运行 workflow meta-test(含改动的 qwen-pr-review-workflow.test.js)的 Linux unit 套件仍在运行,integration / web-shell / TUI-parity 亦然。36 个 skipped 是 review-lane job(非 pull_request 事件触发)、macOS/Windows 套件、以及沙箱 verify/tmux 通道;此处跳过属预期,非信号。由于 unit 套件仍在跑,我尚不宣称 meta-test 在 CI 上通过——下表是实时快照,finalize job 会在 CI 落定后重写它。

沙箱通道(2b-bis)——此处明确不适用。 核心主张是 GitHub Actions 事件 gate("请求有效 bot 现在会启动 review job,而非全部跳过"),并非产品运行时行为。@qwen-code /verify 与 @qwen-code /tmux 驱动的是 CLI 产品,无法演练 base 分支上的 pull_request_target reviewer-request gate,点名它们只是噪音。真正能佐证改动的,是解析该 gate 的 meta-test(见上)加上我在 Stage 1 独立复核的 API 身份事实。剩余的 live 端到端触发本质上只能在合并后观测——pull_request_target 从 base 分支读取 workflow——作者已如实说明;这不是合并前通道能弥补的缺口。

真实场景测试(2c):N/A。 无人值守 CI 运行,且这是 CI/workflow 改动,无 CLI、TUI、Web UI 或 Web Shell 界面——没有可供驱动的用户可见面。

— Qwen Code · qwen4-max

Reviewed at de64fd1ac96cc6f72be73e0d29f5ba180ab64fb8 · re-run with @qwen-code /triage

@qwen-code-review-bot

Copy link
Copy Markdown
Collaborator

Confidence: 5/5 — clean across every stage; a minimal, independently-verified fix I would merge without hesitation once CI is green.

Stepping back: the problem is proven (I re-ran the API checks myself — old account 404, new account a live User, and the cited pull_request_target run with all nine jobs skipped), the fix is the smallest thing that resolves it (four identity sites plus their fixtures), and it is internally consistent end to end. The meta-test parses the gate constant rather than paraphrasing it, so the suite actually pins the change; no other dependent suite is left asserting the old login. The author scoped deliberately to the manual re-review channel and documented every out-of-scope consumer and the post-merge-only nature of the live trigger — that is the kind of boundary-setting that makes a PR easy to maintain, not curse at, six months from now. My independent proposal matched the diff; I found no simpler path it missed and no correctness, security, or regression concern.

This is not a pushover approve: the burden of proof was on the author and it was met with evidence I could and did verify independently, not with framing. The only thing I cannot confirm pre-merge is the live end-to-end trigger, which is inherent to pull_request_target reading the base branch — not a defect in this PR.

The fork-refactor guardrail does not apply (same-repo, fix(ci) type; author has admin access), and Stage 0 raised no escalation. CI has no failures, but the Linux unit suites that run the meta-tests are still in flight (2 pull_request runs pending). So I am not posting an approval against a result that does not exist yet: approval deferred until CI lands green on de64fd1ac96cc6f72be73e0d29f5ba180ab64fb8. The finalize workflow will post the commit-pinned approval once every check on that commit completes green, and withhold it if anything lands red or the head moves.

中文说明

置信度:5/5 —— 各阶段均干净;这是一个最小化、且经独立核实的修复,CI 转绿后我会毫不犹豫地合并。

整体来看:问题已被证明(我亲自复核了 API——旧账号 404、新账号为有效 User、所引用的 pull_request_target run 全部九个 job 跳过);修复是解决它的最小改动(四处身份位点及其 fixture);且端到端内部一致。meta-test 解析的是 gate 常量而非复述它,因此套件真正钉住了改动;没有其他依赖套件仍断言旧 login。作者刻意将范围限定在手动 re-review 通道,并记录了每一个不在范围内的消费者、以及 live 触发只能在合并后观测的性质——这种边界设定让 PR 在六个月后易于维护,而非招人抱怨。我的独立方案与 diff 一致;未发现它遗漏的更简路径,也无正确性、安全或回归顾虑。

这不是"老好人"式批准:举证责任在作者,而他以我能且确实独立核实的证据满足了它,而非靠话术。合并前唯一无法确认的是 live 端到端触发,这是 pull_request_target 从 base 分支读取 workflow 的固有性质——并非本 PR 的缺陷。

fork-refactor 护栏不适用(同仓库、fix(ci) 类型;作者具 admin 权限),Stage 0 也未升级。CI 无失败,但运行 meta-test 的 Linux unit 套件仍在跑(2 个 pull_request run 待完成)。因此我不会对一个尚不存在的结果给出批准:批准推迟到 CI 在 de64fd1ac96cc6f72be73e0d29f5ba180ab64fb8 上转绿。finalize workflow 会在该 commit 的所有 check 绿后发布绑定 commit 的批准;若有任一项转红或 head 移动,则扣留批准。

— Qwen Code · qwen4-max

Reviewed at de64fd1ac96cc6f72be73e0d29f5ba180ab64fb8 · re-run with @qwen-code /triage

@qwen-code-review-bot qwen-code-review-bot left a comment

Copy link
Copy Markdown
Collaborator

Choose a reason for hiding this comment

The reason will be displayed to describe this comment to others. Learn more.

Reviewed. Suggestions are inline.

Not fully linted (tool limitation, not a blocker): .github/workflows/qwen-code-pr-review.yml — actionlint ran workflow-level checks; embedded run: shell deferred (source mapping not yet supported).

中文说明

已审查。 建议见行内评论。

未完整检查(工具限制,非阻断):.github/workflows/qwen-code-pr-review.yml——actionlint 已运行 workflow 级检查;内嵌 run: shell 延迟处理(源映射尚未支持)。

— deepseek-v4.1-flash-1017 via Qwen Code /review (v0.27.4)

id: 'values'
run: |-
echo "bot_login=qwen-code-ci-bot" >> "$GITHUB_OUTPUT"
echo "bot_login=qwen-code-review-bot" >> "$GITHUB_OUTPUT"

Copy link
Copy Markdown
Collaborator

Choose a reason for hiding this comment

The reason will be displayed to describe this comment to others. Learn more.

[Suggestion] R1-1: The review bot's login is now a bare literal at four sites in this workflow, so the next time the account is renamed the manual re-review lane goes silently dead again — the exact failure mode this PR exists to fix. qwen-autofix.yml:75 already keeps the same kind of identity behind a repo variable (AUTOFIX_BOT: "${{ vars.AUTOFIX_BOT_LOGIN || 'qwen-code-dev-bot' }}"), and issue #16832's triage thread recommends that shape here. Without it, a future rename leaves the three gates comparing against a login nobody holds: the review_requested run still starts, every job reports skipped rather than failing, and the meta-test stays green because botLogin is parsed out of this very bot_login line and then asserted against itself.

Witness:

witness: not run — `review scratch-tree` refused (available: false: repo-local includeif credentials config the screen could not read to the bottom), so no isolated probe was possible and the shared worktree was not edited. Confirmation rests on source facts a probe could not add to: grep finds zero occurrences of vars.REVIEW_BOT_LOGIN in the tree, and scripts/tests/qwen-pr-review-workflow.test.js:40 parses bot_login=([A-Za-z0-9-]+) out of the same line its :3457 assertion pins.

A sketch (all four sites plus the test move together):

# job-level if: expressions — vars is available here, env is not
(github.event.action != 'review_requested' ||
 github.event.requested_reviewer.login == (vars.REVIEW_BOT_LOGIN || 'qwen-code-review-bot'))

# review-config output
          echo "bot_login=${{ vars.REVIEW_BOT_LOGIN || 'qwen-code-review-bot' }}" >> "$GITHUB_OUTPUT"

scripts/tests/qwen-pr-review-workflow.test.js extracts the login with /bot_login=([A-Za-z0-9-]+)/, so the indirection needs the extractor reworked to resolve the variable form rather than read a literal — and the four-sites-agree assertions retargeted at the shared source. Note this is a sketch, not an exercised change.

scripts/tests/qwen-pr-review-workflow.test.js — the resolves the bot login from review-config, not a paraphrase test must assert the login resolves through the variable with the literal only as fallback; removing the indirection and re-pinning a bare literal must turn it red. Today no assertion pins that property.

The identity must stay resolvable without needs.review-config.outputs.bot_login, because line 236 is review-config's own gate and the job that publishes that output cannot consume it.

— deepseek-v4.1-flash-1017 via Qwen Code /review

中文说明

[建议] 评审 bot 的登录名现在在本 workflow 的四个位置都是裸字符串,因此账号下次改名时,手动重新评审通道会再次静默失效——正是本 PR 要修的那种故障。qwen-autofix.yml:75 已经把同类身份放在 repo variable 后面(AUTOFIX_BOT: "${{ vars.AUTOFIX_BOT_LOGIN || 'qwen-code-dev-bot' }}"),issue #16832 的 triage 评论也建议这里采用同样的写法。不这样做的话,将来改名会让三个 gate 继续比对一个人人都不持有的登录名:review_requested run 仍会启动,所有 job 报 skipped 而不是失败,meta-test 也照样是绿的——因为 botLogin 就是从这一行 bot_login 里解析出来的,然后再拿它和自己断言。

证据:witness: not run —— review scratch-tree 拒绝创建(repo-local includeif 凭据配置无法完整读取),因此无法做隔离验证,也没有改动共享 worktree。结论基于源码事实:全树 grep 不到 vars.REVIEW_BOT_LOGIN,而 scripts/tests/qwen-pr-review-workflow.test.js:40 用 bot_login=([A-Za-z0-9-]+) 解析的正是 :3457 断言所固定的同一行。

改法示意(四个位置加测试需要一起改):

# job 级 if 表达式——此处可用 vars,不可用 env
(github.event.action != 'review_requested' ||
 github.event.requested_reviewer.login == (vars.REVIEW_BOT_LOGIN || 'qwen-code-review-bot'))

# review-config 的输出
          echo "bot_login=${{ vars.REVIEW_BOT_LOGIN || 'qwen-code-review-bot' }}" >> "$GITHUB_OUTPUT"

scripts/tests/qwen-pr-review-workflow.test.js 用 /bot_login=([A-Za-z0-9-]+)/ 提取登录名,所以引入间接层时需要同时改写提取器,让它解析变量形式而不是读字面量,并把「四处一致」的断言改为指向同一来源。注意这只是示意,并未实际执行验证。

scripts/tests/qwen-pr-review-workflow.test.js 中 resolves the bot login from review-config, not a paraphrase 这个测试应断言登录名经由变量解析、字面量仅作 fallback;把间接层去掉并重新写死字面量时该测试必须变红。目前没有任何断言固定这一点。

该身份必须能在不依赖 needs.review-config.outputs.bot_login 的情况下解析出来,因为第 236 行正是 review-config 自己的 gate,发布该输出的 job 无法消费它。

— deepseek-v4.1-flash-1017 via Qwen Code /review (v0.27.4)

@qwen-code-review-bot

Copy link
Copy Markdown
Collaborator

CI Failure Patrol: this failure could not be confidently classified: Log only shows the aggregate gate (BUILD success, SHARDS failure); no failing test or transient error is named, so nothing supports a rerun or a PR-caused verdict.

No automatic action was taken. Inspect the failed job before rerunning or updating the branch.

中文说明

CI 失败巡逻:无法确信归类此失败:日志只有汇总判定(BUILD 成功、SHARDS 失败),未指出具体失败测试或瞬时错误,无法支持重跑或归因于 PR 的结论。

未采取自动动作。请先人工查看失败 job,再决定重跑或更新分支。

@qwen-code-review-bot

Copy link
Copy Markdown
Collaborator

CI Failure Patrol: this failure could not be confidently classified: Deterministic 'ru' settings coverage assertion (2 missing entries) unrelated to the CI-workflow files this PR touches; no causal link and no transient evidence.

No automatic action was taken. Inspect the failed job before rerunning or updating the branch.

中文说明

CI 失败巡逻:无法确信归类此失败:确定性的 'ru' 设置覆盖断言失败(缺少 2 个条目),与本 PR 改动的 CI 工作流文件无关,既无因果关系也无瞬时故障证据。

未采取自动动作。请先人工查看失败 job,再决定重跑或更新分支。

@wenshao

wenshao commented Nov 19, 2026

Copy link
Copy Markdown
Collaborator

PR 17848 round 1 verification — Verdict: merge-ready — 85/85 scripted assertions passed, 0 failed. Verified head: de64fd1ac96cc6f72be73e0d29f5ba180ab64fb8 (base bd8926d196227005d10648fa29edac6bc28504d2; the two changed files are byte-identical between the PR's parent 933497af52 and that base tip). Review state: 1 open thread, a non-blocking [Suggestion], measured; 0 open blocking threads. CI at this head is red on 2 checks, whose root is a deterministic ru settings-coverage assertion in Linux unit tests (shard 1/2) — files this diff does not touch; raw logs are unreachable from this host and that job was not re-run locally (see CI state).

中文摘要

结论:merge-ready。 85 项脚本化断言全部通过,0 失败。验证的 head 为 de64fd1a。

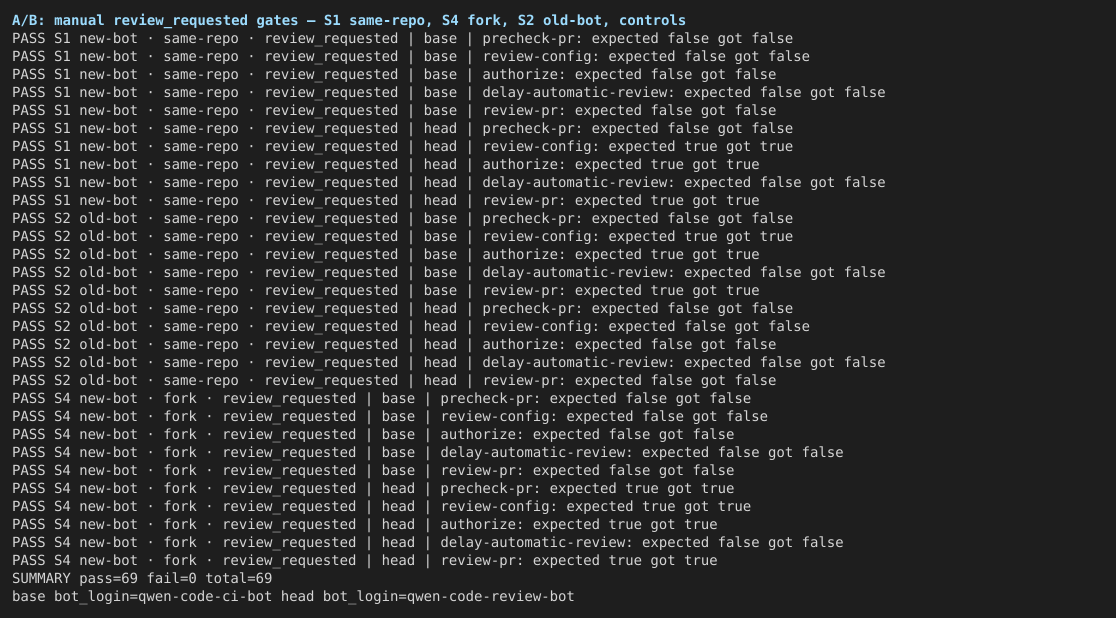
A/B 结论(见 01-gate-ab-matrix.png): 用 GitHub Actions 表达式语义逐条求值 workflow 的 job if:。同一个 review_requested 事件、同一个请求者(wenshao,admin):

场景 base 启动的门 head 启动的门
S1 同仓库 PR,请求 qwen-code-review-bot 0/3(review-config、authorize、review-pr 全 false;precheck 按设计只跑 fork) 3/3
S4 fork PR,请求 qwen-code-review-bot 0/4 4/4
S2 请求旧账号 qwen-code-ci-bot(今天已 404,事件不可产生) 3/3 0/3
S3 请求人类 reviewer;S5 opened;S6 synchronize 与 head 完全一致(无回归) 同左

S2 的 base 3/3 是求值器的正控制:它证明这些门不是恒 false,base 的 0/3 是登录名不匹配造成的。PR 引用的真实 run 44522592919(pull_request_target)9 个 job 全是 skipped,与 base 臂预测一致。

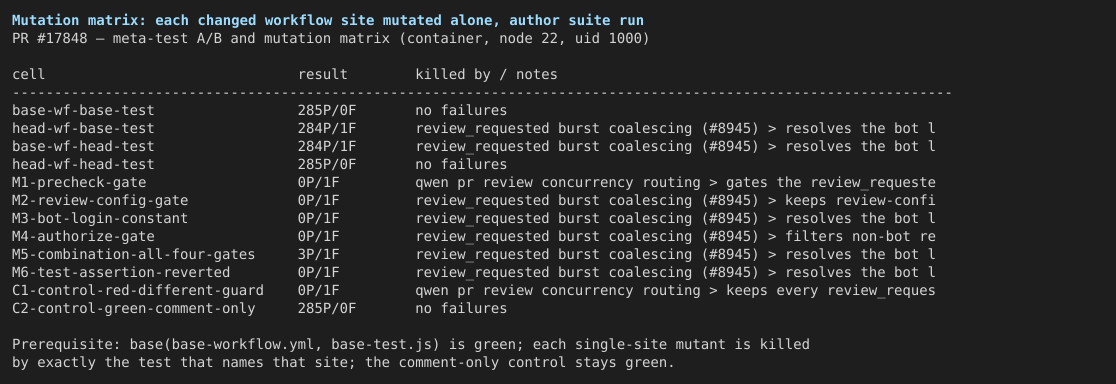
变异矩阵(见 02-mutation-matrix.png): 作者套件 head 285/285 通过;base 文件对 base 测试 285/285 通过;把 head 测试放到 base workflow 上、或把 base 测试放到 head workflow 上,都恰好红在 resolves the bot login from review-config, not a paraphrase。四个改动点各自单点回退,都被点名对应测试杀死;四处同时回退只剩字面量断言变红(说明三处 gate 测试是与同一文件里的 bot_login 自比对);另做的“同一文件另一个守卫”正控制能变红、只改注释的负控制仍 285/285 绿。

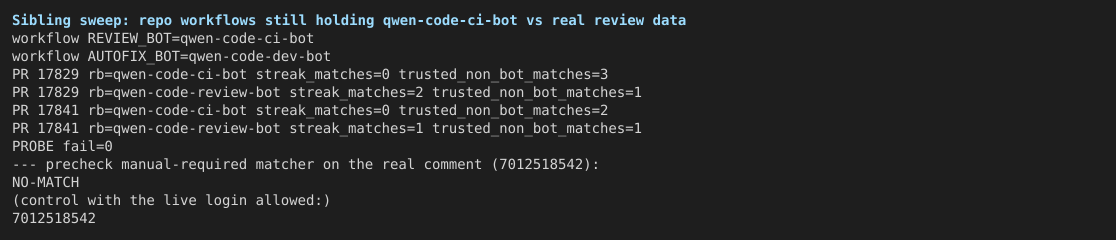
非阻断观察(本 PR 之外、既有问题): 仓库里其他 workflow 仍持有已删除的 qwen-code-ci-bot。用真实 review 数据跑 qwen-autofix.yml 自己的选择器:交付值 REVIEW_BOT=qwen-code-ci-bot 匹配到 0 条,真实账号匹配到 2 条(PR 17829);qwen-pr-safety-precheck.yml 的 manual-required 评论归属匹配器对真实评论(作者 qwen-code-review-bot,type User)返回空,把真实登录加入白名单后返回该评论 id。这些不是本 PR 引入,本 PR 也明确声明不修;但 PR 描述里“被 collaborator association 分支掩盖”的说法只对自动修复的部分过滤成立,对这两处不成立,见 Corrections。

未覆盖: 合并后的 live 触发无法在合并前证明(pull_request_target 读 base 分支的 workflow);review-artifact-upload 与 review-worktree-cleanup 两个套件因本轮树未为本 head 构建(core 的 dist 缺失)无法收集;依赖套件整体跑时有 2 个 test 在负载下超时,但它们在 head 与 base 单独跑都通过(A/A)。

Central claim and A/B

Claim. The manual review_requested lane in .github/workflows/qwen-code-pr-review.yml compared the requested reviewer against qwen-code-ci-bot at three sites and published that login from review-config; the account is gone (GET /users/qwen-code-ci-bot → 404), so a request for the live qwen-code-review-bot produced a run in which every job skipped. At head all four sites name the live account, so the same request starts the lane.

Instrument. gate-eval.mjs parses each revision's workflow, extracts the five job-level if: expressions that gate the lane (precheck-pr, review-config, authorize, delay-automatic-review, review-pr), and evaluates them with an implementation of the GitHub Actions expression language (loose equality, case-insensitive strings, truthiness, format/fromJSON/contains/startsWith, !cancelled()), threading needs.*.outputs between jobs exactly as GitHub does (a skipped job contributes an empty output). Facts the expression language cannot supply were captured live and are asserted in the same harness: account status, collaborator permission, the author of a real review and its author_association, and the cited run's job conclusions.

scenario (requester = wenshao, admin) gates that evaluate true, base head oracle
S1 same-repo PR, review_requested → qwen-code-review-bot 0/3 3/3 review-config, authorize, review-pr
S4 fork PR, review_requested → qwen-code-review-bot 0/4 4/4 + precheck-pr (fork-only by design)
S2 same-repo, review_requested → qwen-code-ci-bot (event not producible today) 3/3 0/3 positive control: the gates are not always-false
S3 same-repo, review_requested → human chiga0 0/3 0/3 unchanged sibling filtering
S5 opened, S6 synchronize (same-repo) 3/3 3/3 lifecycle path unchanged

Two independent witnesses support the base arm beyond the evaluator: the cited Actions run 44522592919 is a pull_request_target run whose 9 jobs are all conclusion: skipped, and the evaluator's S2 control flips the same expressions to true at base, so the S1/S4 zeros are attributable to the login literal rather than to a dead evaluator.

A/B evidence: evidence/01-gate-ab-matrix.png (the matrix as it printed, headline cells plus controls).

A/B gate matrix

Mutation evidence: evidence/02-mutation-matrix.png — every cell is the author's suite run against one single-point mutation, restored and sha256-checked before the next row.

mutation matrix

Reviewer Test Plan, step by step

  1. Identity evidence — measured. Old account 404; qwen-code-review-bot is a User (id 40956131) with write permission (collaborators/.../permission → {"permission":"write"}); PR 17841's review by that account carries author_association: COLLABORATOR.
  2. No old references, four sites agree — measured. qwen-code-ci-bot occurs 4× at base and 0× at head in the workflow; the four sites (precheck-pr.if, review-config.if, the bot_login output, authorize.if) all named the new login at head, and review-pr.if (line 502) consumes needs.review-config.outputs.bot_login, so it agrees by construction.
  3. Run the meta-test — 285 passed / 0 failed in the container (the author's 282/3-skipped was macOS; the three extra passes here are Linux-only tests).
  4. Dependent suites — grep -R finds 7; 5 were run in one invocation: 304 passed, 2 timed out under load. Both timed-out tests pass individually on head and on base (A/A), so they are environmental. Two suites (review-artifact-upload, review-worktree-cleanup) could not collect because they import @qwen-code/qwen-code-core through its dist entry and this tree was not built for this head — recorded under Not covered.
  5. Post-merge live trigger — not run, and not runnable pre-merge: pull_request_target executes the base branch's workflow. This is the one step the round cannot falsify; see Not covered.

Existing review findings

review-threads.json: 1 thread, unresolved, not outdated, author association COLLABORATOR, tagged [Suggestion] — so it is not a blocking thread under the contract. 0 standing change requests.

thread reviewer claim status at head
R1-1 (qwen-code-pr-review.yml:245) review bot The login is a bare literal at four sites, so the next rename kills the lane again; suggests a repo variable as qwen-autofix.yml already does for AUTOFIX_BOT. Says the meta-test stays green because botLogin is parsed from the same line. No defect claimed (robustness suggestion). Premises verified: 4 bare literals, no vars.REVIEW_BOT_LOGIN in the tree, botLogin parsed from the bot_login line. Nuance measured: one assertion does pin the literal, so a complete revert is caught (row M5) — what no test can see is whether a newly written login is a live account.

Corrections

The PR description's scope justification says the untouched consumers are "separate consumers or are masked by the collaborator association branches". Measured, that holds for part of qwen-autofix.yml and not for the rest:

  • The review-count filters (N_REVIEWS, N_COMMENTS) select on (.author_association | IN($trust[])) or (.user.login == $rb), so the COLLABORATOR association does mask the stale $rb there.
  • The convergence-streak selector matches .user.login == $rb with no association clause. On real review data (PR 17829: two qwen-code-review-bot reviews), the shipped constant matches 0, the live login matches 2.
  • qwen-pr-safety-precheck.yml's manual-required comment ownership has no association branch at all: it accepts github-actions[bot], qwen-code-ci-bot, or user.type == "Bot". The live bot is a User named qwen-code-review-bot, so the matcher returns empty for its own real comment (id 7012518542) and returns that id only when the live login is added.

This is a correction to the description's mechanism, not a request to widen this PR: the manual re-review lane itself is complete, and the manual lane on owned PRs never runs precheck-pr (fork-only). Evidence: evidence/03-sibling-identity-probe.png.

sibling identity probe

Non-blocking observations (pre-existing, outside this diff)

  1. qwen-autofix.yml / qwen-autofix-fork-bridge.yml keep REVIEW_BOT: 'qwen-code-ci-bot'. Consequences measured above: the convergence-streak counter can never match a live review, and the human-watermark exclusion treats the bot's COLLABORATOR reviews as human activity. Not introduced by this PR; the description explicitly defers it.
  2. qwen-pr-safety-precheck.yml manual-required comment upsert. With the live bot posting through CI_BOT_PAT, the "Upsert" step cannot find the existing comment, so a manual_required decision posts a new comment each run, and allow_triage cannot clear the stale one. Reachable only through fork PRs, where precheck-pr runs.
  3. pr-force-push-reminder.yml still lists the old login in its automation exclusion; cosmetic.
  4. The three gate-sync tests are self-referential: they compare each gate against botLogin parsed from the same file. Row M5 shows the consequence — reverting all four sites together leaves only the hard-coded literal assertion red.

CI state at the verified head

gh pr checks 17848 reports Linux unit tests (shard 1/2) → fail (11m11s) and Test (ubuntu-latest, Node 22.x) → fail (9s, the aggregate over the shards); the rest of the matrix, including Lint & Static, Linux unit tests (shard 2/2) and both integration shards, passed on the same head. The repository's CI Failure Patrol comments on this PR classify the root failure as a deterministic ru settings-coverage assertion (2 missing entries) "unrelated to the CI-workflow files this PR touches". The raw job log is on Azure blob storage, which this host cannot reach (TLS handshake timeout), so the failing test was not re-run locally; that classification is the patrol's, not this round's measurement. Nothing in this diff touches locales, settings coverage, or packages/cli, and the PR's own affected suite is green here.

Not covered

  • The post-merge live trigger. pull_request_target runs the base branch's workflow, so no pre-merge execution can prove the run starts; the PR's own step 5 says the same.
  • review-artifact-upload.test.js and review-worktree-cleanup-workflow.test.js — not collected: they resolve @qwen-code/qwen-code-core through dist, and the reused node_modules (hardlinked from a different checkout) carries playwright-core 1.58.2 where this tree expects the bundled 1.62.1, so npm run build fails before core is produced. Both suites assert on artifact/cleanup steps this diff does not touch.
  • Two dependent tests time out in the aggregate run (qwen-resolve-workflow > allows wrapped gh review writes…, qwen-triage-workflow > screens sponsored runs…). Each passes individually at head and at base; the round records the aggregate coverage as lost rather than as a failure.
  • actionlint is not available in the container, matching the author's note that it is unusable on this workflow.
  • qwen-autofix-workflow.test.js was not run: the author reports a pre-existing 120-second timeout in it, and the file needs the same missing build.

Methodology

Boundary. node:22-bookworm container, --user 1000:1000, HOME=/tmp/qwen-home, mounting the standalone PR clone at /work, the trusted main scripts read-only at /trusted-scripts, the base commit's .qwen read-only over /work/.qwen, and the gh metadata snapshot read-only at /verify-context. No host HOME, no SSH keys, no gh token, no model proxy; attested with QWEN_VERIFY_CREDENTIAL_FREE=1 after the trusted credential scan, gate record in boundary-gate.json.

The gate A/B is gate-eval.mjs run over base-workflow.yml (git show <base>:.github/workflows/qwen-code-pr-review.yml) and head-workflow.yml (the PR tree). The mutation matrix is mutate.mjs: it swaps the two changed files between their base and head blobs for the four whole-file cells, then applies one single-point mutation per changed workflow site, runs the author's suite, restores the tree, and verifies the restored sha256 before the next row; C1/C2 are the red/green controls. The sibling probe (sibling-probe.sh) applies the autofix workflow's own selector shapes to review objects fetched from the API, and evaluates the precheck comment matcher verbatim against a real comment. Targeted gates ran the affected suite and five dependent suites with the repo's scripts/tests/vitest.config.ts. Raw logs and the JSON results live beside this report (suite-head.log, gates-dependent.log, log-*.log, gate-eval.json, mutations-raw.json, sibling-probe.log). jq was installed into the container because the image does not ship it and the workflow scripts call it; without it the suite reported 48 failures, all environmental.

— DeepSeek-V4.1-Flash-1017@fda99a87 via Qwen Code /verify-pr (v0.28.0; skill eeebc98be317)

@wenshao

wenshao commented Nov 19, 2026

Copy link
Copy Markdown
Collaborator

评审完成,主检出未受影响。以下为正式评审结论(将作为评论发布):

Review summary — no blocking issues

Reviewed at head de64fd1a (2 files, +25/−15). The manual review_requested lane now names the live account at every site, and the swap is internally consistent. Independently verified on Linux, read-only API checks, and executed meta-tests; no Critical and no new Suggestion.

Verified at this head

  • Complete, consistent swap. All four literal sites — precheck-pr.if (:106), review-config.if (:236), the bot_login output (:245), authorize.if (:342) — read qwen-code-review-bot; review-pr.if (:502) consumes needs.review-config.outputs.bot_login and agrees by construction. Zero qwen-code-ci-bot references remain in the workflow, and the KEEP IN SYNC sites moved together. The remaining bot_login occurrences are runtime gh api user credential lookups, independent of the constant.
  • Identity evidence re-checked live. GET /users/qwen-code-ci-bot → 404; qwen-code-review-bot resolves as a User (id 40956131) with write collaborator permission — requestable as a reviewer, and the observed PR review author.
  • Meta-tests executed. Changed suite: 285/285 passed. Dependent suites per the AGENTS.md rule (qwen-resolve, qwen-triage, review-artifact-upload, review-worktree-cleanup): 325/325 passed. qwen-autofix-workflow: 356/357 — the single failure (aborts the scan and command lanes … gh config dir cannot be minted) reproduces with the identical signature on the merge-base tree 933497af, and both of its inputs (qwen-autofix.yml, the test file) are outside this diff: pre-existing host-specific, not introduced here.
  • Static gates. actionlint workflow-level checks: 0 findings on changed lines (embedded run: shell deferred — tool limitation, non-blocking). prettier --check on both changed files and git diff --check: clean.

CI state — inherited red, already fixed on main. The two red checks (Linux unit tests (shard 1/2) and its aggregate Test (ubuntu-latest, Node 22.x)) share one root: the deterministic ru settings-coverage assertion. The same signature is red on main run 41f98a638d; the missing entries arrived with #17830 and were fixed on main by #17858 (adca3e7ddc, main CI now green). Both commits postdate this PR's merge-base, and the two changed files have zero drift against the current main tip — merging main clears the red without conflict.

Existing non-blocking items (not re-reported)

  • R1-1 (open inline Suggestion): the login remains a bare literal at four sites; a repo-variable indirection (vars.REVIEW_BOT_LOGIN || …, as qwen-autofix.yml does for AUTOFIX_BOT) would survive the next rename. Its premises still hold at this head — valid follow-up, not a blocker for this fix.
  • The round-1 verification report's Corrections still stand: the description's "masked by the collaborator association branches" holds for the autofix review-count filters but not for the convergence-streak selector or the precheck manual-required comment matcher. Those consumers are pre-existing and explicitly out of scope; tightening the scope wording is optional.

Residual. The live trigger is inherently post-merge-only (pull_request_target reads the base branch's workflow); the author's test-plan step 5 covers it.

Verdict: no blocking issues — consistent with the round-1 verification (merge-ready, 85/85 assertions) and triage's approve-on-green. Merge main to pick up the CI fix.

中文摘要

结论:无阻塞问题。 在 head de64fd1a 独立复核:四处字面量与 bot_login 输出全部指向 qwen-code-review-bot,review-pr.if 经输出间接一致,workflow 内无旧账号残留,KEEP IN SYNC 各点同步改动。线上只读核验:旧账号 404,新账号为 write 协作者、可被请求为 reviewer。Linux 实测:改动套件 285/285,四个依赖套件 325/325,autofix 套件 356/357——唯一失败在 merge-base 树 933497af 上同签名复现,且其两个输入均不在 diff 内,属本机既有问题。actionlint 改动行 0 发现(内嵌 shell 延迟检查为工具限制,非阻塞),prettier 与 git diff --check 干净。

CI 两红为继承红:main run 41f98a638d 同签名,根因是 #17830 引入的 ru 词条缺口,main 已由 #17858(adca3e7ddc)修复且 CI 转绿;两个改动文件对当前 main tip 零漂移,合入 main 即消。

既有非阻塞项不重复报告:R1-1(repo variable 间接层建议)前提在本 head 仍成立,可作跟进;一轮验证报告的 Corrections(「被 collaborator association 掩盖」仅部分成立)仍有效,所涉消费者均为既有且明确不在本 PR 范围,描述措辞可选收紧。live 触发只能合并后观测,作者测试计划第 5 步已覆盖。

This branch has not been deployed

No deployments
Sign up for free to join this conversation on GitHub. Already have an account? Sign in to comment

Labels

review/self-reported The linked issue was opened by the PR author (self-reported)

Projects

None yet

Development

Successfully merging this pull request may close these issues.

ci: manual PR re-review channel is dead — qwen-code-pr-review.yml gates on qwen-code-ci-bot, an account that no longer exists (404)

3 participants