Repository navigation
fix(core): report a cancelled shell as interrupted, not completed - #15836
Conversation



The shell tool kills the process group on a user cancel but returns an
ordinary result, so the scheduler's post-execute cancellation branch labelled
the call "already completed" and told the model not to retry work that never
finished. Let producers mark that outcome on the result; the shell tool sets it
on a non-timeout, non-promote-refused abort.

Closes QwenLM#15833


|
Verdict: 中文摘要(点击展开)结论:
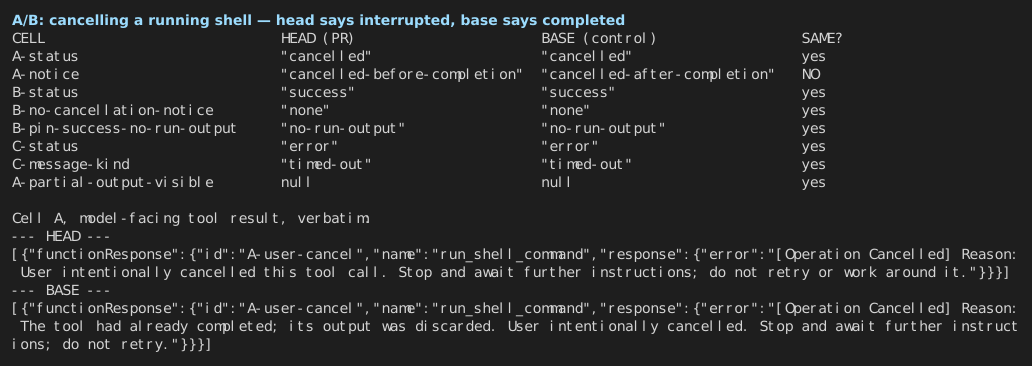
The central claim and the A/BClaim under test: a shell killed by a user cancel must reach the model as interrupted mid-work, not as finished and discarded. Both arms run the same harness (copied verbatim into each tree) against their own compiled
Only the cancel notice moves; every neighbouring outcome is byte-identical between arms, which is the check that the PR did not relabel results generally.
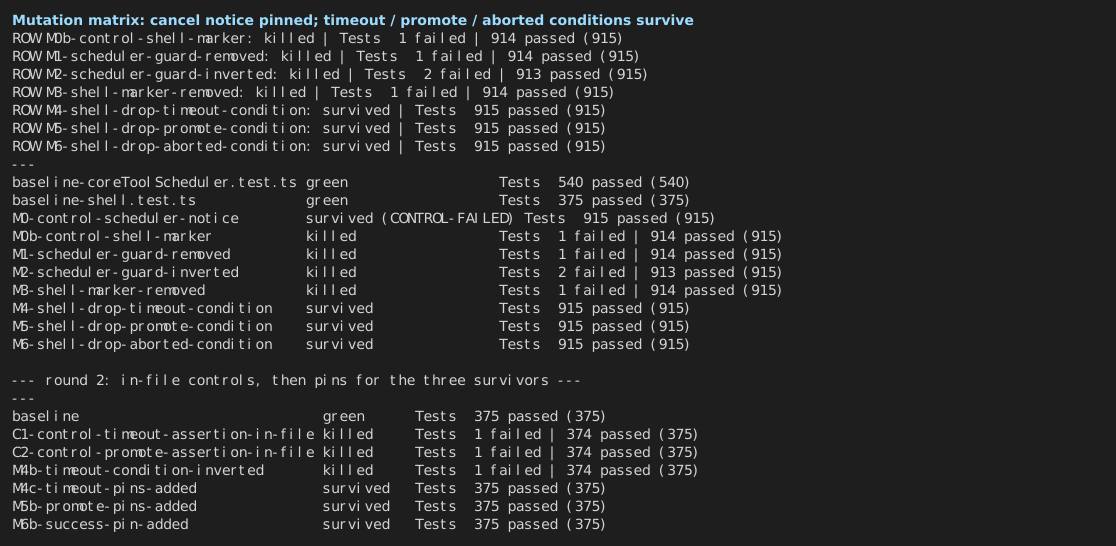
The two wire payloads, verbatim: Findings1. Minor — the fix drops the partial output the model used to see, for the very case it fixesBefore the PR the model received the shell tool's own text, which names the work that already ran ( Boundaries measured on both arms: it is not a model-visible regression against base (identical loss), it is not a new code path (both go through 2. Suggestion — three conditions of the new marker are unpinned (coverage gap, not a defect)Round 1, suites
The last row is why round 2 re-landed the controls inside Green on head means the pins are correct but also that the current suite cannot tell you if any of the three conditions were deleted. The suggested addition is the first two assertions, plus a matching delete-condition mutant as the test's own witness.
3. Suggestion — the sibling shape the description defersThe description lists "a call cancelled before it starts" as out of scope. The adjacent shape — the cancel landing while the shell's confirmation dialog is still open in approval mode Not covered
MethodologyTwo worktrees (head at the PR head, base at the base tip), each installed with |
The scheduler replaced the whole model-visible payload with the cancellation
notice, so the output a killed command had already produced disappeared even
though the shell tool reports it. Append the producer's own interrupted text
when it sets interruptedBeforeCompletion, and pin the marker's negative cases
that the existing suites did not distinguish.

|
All three findings are addressed in 1 (Minor — the fix drops the output the model used to see). Taking it; the two properties are separable and now both hold. Nothing changes for a post-completion cancel — that path still discards the output and keeps only the "already completed" notice. The shell test now pins the partial-output sentence too, so a future change that drops it reds the producer's own case. 2 (Suggestion — the three conditions were unpinned). Added the assertions you specified: 3 (Suggestion — the sibling shape). Added a line to Not validated / out of scope: a cancel that lands while the shell's confirmation dialog is open (approval mode
|

|
Thanks for the PR — and for picking this up after offering to in the issue. Template looks good ✓. Every required section is filled in, including a real Tested-on table and an honest Risk & Scope. One small ask, not a gate: the template's trailing Problem is an observed bug, and about as well-evidenced as these get. #15833 is open, carries a deterministic reproduction ( Direction is aligned, and the codebase agrees with it independently. Size: core paths are touched ( Approach is close to minimal and mirrors the existing pattern rather than inventing one. One genuine question for the maintainer, not a blocker: the Risk: Stage 1e matched — Moving on to code review. 🔍 中文说明感谢贡献,也感谢你在 issue 里主动提出可以发 PR 之后真的把它做了。 模板完整 ✓。每个必填小节都写了,包括真实的 Tested-on 表格和坦诚的 Risk & Scope。一个小小的请求(不是拦截项):模板末尾的 问题是已观测到的 bug,证据非常充分。#15833 处于 open 状态,带有确定性复现( 方向是对齐的,而且代码库本身就独立支持这个方向。 规模:触及了核心路径( 方案接近最小改动,并且是照搬既有模式而非另创一套。有一个真正需要维护者判断的问题(不是拦截项): 风险:Stage 1e 命中—— 进入代码审查 🔍 — Qwen Code · qwen3.8-max-2026-09-02 Reviewed at |
Code reviewIndependent proposal first. Reading only the title and the motivation, I'd have ruled out the two obvious alternatives: making the shell tool throw on user abort (it changes the error type, the telemetry span status and the whole response shape, and the issue is explicit that returning is deliberate), and string-matching the shell's own wording in the scheduler (brittle, and exactly the coupling the description says it wants to avoid). That leaves an explicit producer-set signal on the result, written by the tool that knows and read only by the branch that has to decide. That is what this PR does, so it matches my baseline rather than merely being defensible. The marker fires exactly when the tool already says Not a dead switch. Written in The new parameter is placed correctly. One gap worth naming — non-blocking. The signal does not survive the managed-runtime wrapper. sequenceDiagram
participant P1 as User (Esc or Ctrl+C)
participant P2 as CoreToolScheduler
participant P3 as ShellToolInvocation
participant P4 as ShellExecutionService
P1->>P2: abort the turn signal
P2->>P3: execute(signal) already in flight
P3->>P4: kill the process group
P4-->>P3: result.aborted true, plus partial output
P3-->>P2: returns a ToolResult, does not throw
Note over P2: signal.aborted and not a timeout, so the aborted branch runs
P2->>P2: interruptedBeforeCompletion selects BEFORE instead of AFTER
P2-->>P1: cancelled, notice plus what already ran
Files changed (5 of 5 shown)
Test evidence — the PR's own CI, read via the APII did not build or run anything from this PR; the review is static. This is what CI actually recorded on the reviewed commit The headline is that there is no test result on this commit. The I am calling that infrastructure, not the PR: nothing in the step list reached code the diff touches, and a cancelled install is not a failure signal about these five files. But the honest consequence is that zero unit-test evidence exists for the reviewed head, and there are no What did complete is green:
On the earlier A/B run, and precisely how far it reaches. @wenshao's Two limits matter for the current head, and I would rather state them than let the green verdict carry over. First, it verified The author reports Not verified: the unit and integration suites on the reviewed head (CI cancelled before the test step); the new partial-output path end-to-end on Sandboxed verification would settle this: A plain CI re-run on this head is the cheaper first step and would close the largest gap on its own. Real-scenario tmux testing: N/A — this is an unattended CI run ( 中文说明代码审查先给独立方案。 只看标题和动机时,我会先排除两个显而易见的替代做法:让 shell 工具在用户取消时抛异常(这会改变错误类型、telemetry span 状态和整个响应结构,而且 issue 明确说明"返回"是有意为之),以及在调度器里去匹配 shell 自己的措辞(脆弱,而且正是描述中想避免的耦合)。剩下的就是一个由生产者显式设置在结果上的信号——由知情的工具写入,只由需要判断的那个分支读取。这正是本 PR 的做法,所以它符合我的基线方案,而不仅仅是"说得过去"。 标记恰好在工具已经报告 不是死开关。 在 新参数位置正确。 一个值得点名的缺口——非拦截项。 该信号无法穿过 managed-runtime 包装层。 测试证据——PR 自己的 CI,通过 API 读取我没有构建或运行本 PR 的任何内容,审查是静态的。以下是 CI 在被审查提交 结论是:这个提交上没有任何测试结果。 我判定这是基础设施问题,而非 PR 造成:步骤列表中没有任何一步触及 diff 所改的代码,而安装阶段被取消并不是关于这五个文件的失败信号。但诚实的后果是:被审查的 head 上不存在任何单元测试证据,而且该提交上没有在飞的 已完成的检查都是绿的: 关于此前那次 A/B 运行,以及它究竟覆盖到哪里。 @wenshao 在本 PR 上的 对当前 head 而言有两条限制很关键,我宁愿说出来,也不愿让那个绿色结论被顺延过来。第一,它验证的是 作者报告 未验证:被审查 head 上的单元测试与集成测试套件(CI 在测试步骤之前就被取消); 沙箱验证可以定案: 在当前 head 上单纯重跑一次 CI 是更省事的第一步,并且它自己就能补上最大的那个缺口。 真实场景 tmux 测试:N/A——这是一次无人值守的 CI 运行( — Qwen Code · qwen3.8-max-2026-09-02 Reviewed at |
|
Confidence: 3/5 — the code itself I would defend; what caps this is evidence, not design: the reviewed head has no test run at all, and it moved past the commit the A/B validated. ⏸️ Deferring to @yiliang114 (already the assignee, and the Stepping back. The problem is real and it is the kind that matters: telling a model that a half-run migration "had already completed; do not retry" converts a recoverable interruption into a false belief that the work is done. The reproduction in #15833 is unusually good, and the fix is 33 production lines that mirror a distinction the file already makes on the throw path. Going back to my own independent proposal from the review stage, I don't have a simpler one — making the shell throw would be worse, and matching its wording in the scheduler would be worse still. If I inherited this in six months I would thank whoever wrote it: the flag is documented at both ends, and the guard reuses a predicate that already existed rather than adding a second source of truth. So why not approve. Three things, in order of how much they weigh:
The trap here is that this PR is easy to wave through: excellent issue, clean diff, a strong verification report already attached. That report is exactly why the staleness matters — it is good enough that a reader will assume it covers the current head. It does not. What would move me to approve:
@2SinceJuly — none of this is a criticism of the change; items 1 and 3 are largely not yours to fix. Item 1 needs a maintainer to re-trigger CI on a fork PR. 中文说明信心度:3/5 —— 代码本身我愿意为之辩护;把它压到 3 分的是证据,不是设计:被审查的 head 完全没有测试运行记录,而且它已经越过了 A/B 所验证的那个提交。 ⏸️ 转交 @yiliang114(其已是本 PR 的 assignee,并且正是 退一步看整体。问题是真实的,而且是要紧的那一类:告诉模型一个只跑了一半的迁移"had already completed; do not retry",会把一次可恢复的中断变成一个"工作已完成"的错误信念。#15833 的复现质量相当高,而修复只有 33 行生产代码,并且沿用了该文件在抛异常路径上早已做出的区分。回到我在审查阶段写下的独立方案,我没有更简单的做法——让 shell 抛异常更糟,在调度器里匹配它的措辞更糟。如果六个月后由我接手,我会感谢写下它的人:这个标记在两端都有文档说明,而且守卫复用了既有判定式,没有新增第二个事实来源。 那为什么不批准。三件事,按权重排序:
此处的陷阱在于:这个 PR 很容易被挥手放行——issue 优秀、diff 干净、还已经附着一份有力的验证报告。而恰恰因为那份报告足够好,读者会假定它覆盖了当前 head。它没有。 能让我转向批准的条件:
@2SinceJuly —— 这些都不是对改动本身的批评;第 1 条和第 3 条基本不该由你来解决。第 1 条需要维护者为 fork PR 重新触发 CI。 — Qwen Code · qwen3.8-max-2026-09-02 Reviewed at |

|
Thanks for picking this up. I'm not working on a separate PR, so please go ahead. On the evidence gap raised in the stage-3 review (no before/after for the partial-output half): I'm running your head |
|
Results for head One correction to my earlier note: the baseline was the merge-base Interactive TUI, scripted model. The harness pressed Esc or Ctrl+C while the command was running. Scenarios: single call, parallel calls, and a payment script that prints
Real model (Qwen3.8-27B on local llama.cpp). Same TUI. Esc was pressed about 1.5 s into a payment script. A fresh
On this question the model did not take the old notice at face value. With the output discarded, it answered UNKNOWN every time. With the fix it gave a correct definite answer in 10 of 20 runs, and neither build produced a wrong answer. The partial-output half also did not make the model believe that a payment which had landed never happened (0 NO in 10). This differs from the manual repro in #15833: asked "did the command finish?", the model said yes on the old build. Not covered: macOS and Windows, the managed-runtime path from the stage-3 review, and models other than this one. |
|
Thanks @stars-spark — this fills the evidence gap the stage-3 review flagged for the partial-output half. The numbers line up with the intended behaviour:
The environments you list as uncovered (macOS/Windows, the managed-runtime path, models other than Qwen3.8-27B) stay out of scope for this PR; the existing "Not validated / out of scope" section already says the managed path is untested, and I would rather leave them uncovered than claim coverage. Re-requesting review on the current head |
|
Thanks @stars-spark — the head-level table closes the gap the stage-3 review called out, and thanks for correcting the baseline to the merge-base build. With Two things still lack coverage, and I want to be explicit rather than let the green table imply otherwise: managed-runtime, and Windows. On managed-runtime — I did not take the whitelist route. Adding On CI — the run for One decision I should not make alone: whether keeping the partial pre-kill output inside this PR is wanted at all. It is separable from the notice fix — landing only the notice change is a complete, well-evidenced PR on its own — so I am happy to split it if that is the maintainer's preference. |

|
Checked the fix against the other producers that signal interruption by returning, and there are three siblings the The scheduler's cancel path picks
Each of these is "interrupted before completion" in the same sense as the killed shell: the unit of work did not finish. So either they should set I have not changed anything here since this PR already owns the flag and the message split. Happy to send the sibling follow-up once this lands, or fold the three into this PR if you would rather cover the class in one go. |
The monitor, create_sub_session, ask_user_question and workflow tools
report a cancelled call by returning a result instead of throwing, so
the scheduler's returned-means-finished assumption told the model the
work had completed. They now set interruptedBeforeCompletion, which the
scheduler already honours for the shell tool.
|
Good catch — all of them return on cancel, so the scheduler's returned-means-finished read was wrong for each. Fixed in
I kept the flag opt-in instead of flipping the default. The scheduler only reads it when the turn's signal is aborted, so a plain dialog decline is unchanged, and the producers that genuinely finish despite a late abort (the shell's timeout / promote-refused paths now pin this) keep saying "already completed". Each producer has an assertion on the flag, and Verification on |
|
Verdict: 中文摘要(点击展开)结论:
Previous round's findings
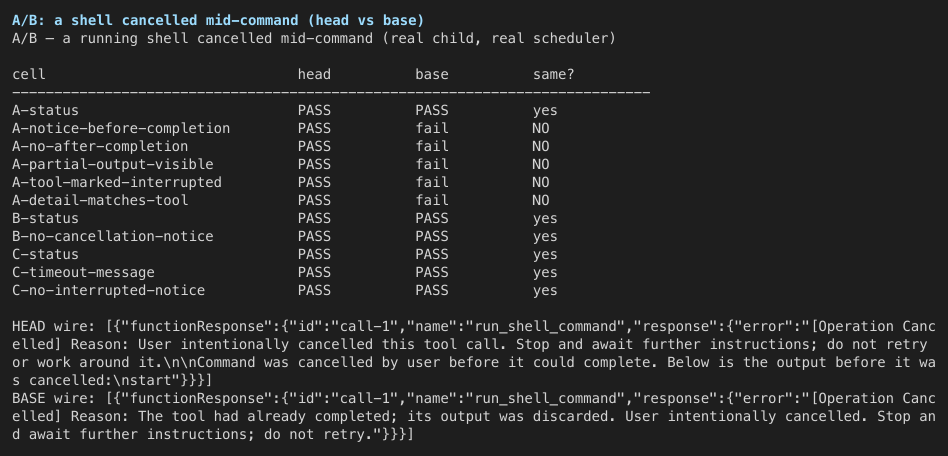
The central claim and the A/BClaim under test: a shell killed by a user cancel must reach the model as interrupted mid-work, and the model must keep the output the command produced before the kill. Both arms run the same harness against their own compiled
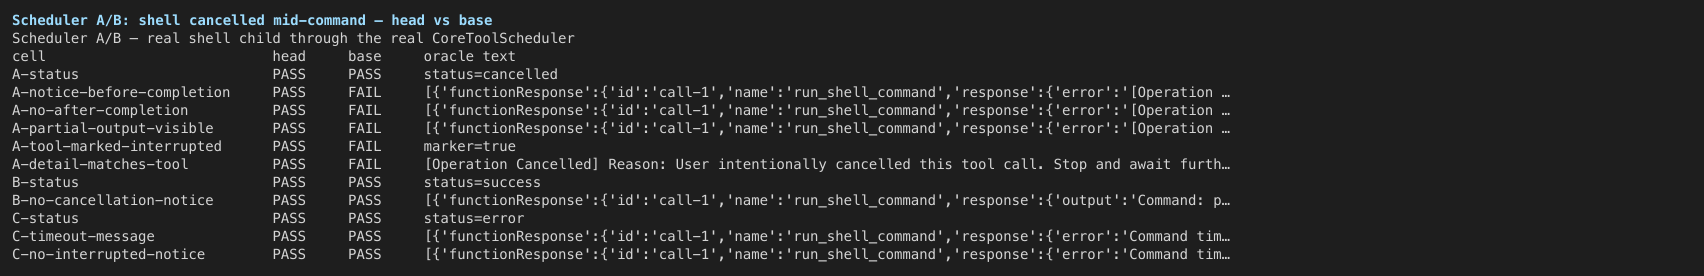
Head 11/11 cells pass; base fails exactly the five cancel cells and matches on every neighbouring outcome (B, C), which is the check that the PR did not relabel results generally.
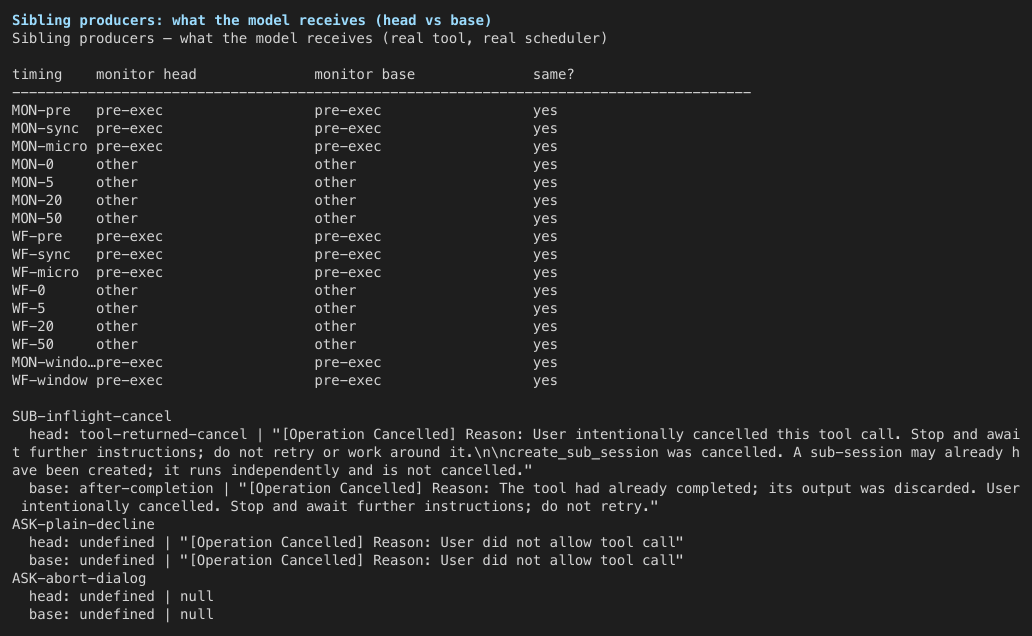
The two wire payloads, verbatim: Sibling producers added in
|
| Cell | Head | Base |
|---|---|---|
create_sub_session cancelled mid-spawn |
User intentionally cancelled… + create_sub_session was cancelled. A sub-session may already have been created; it runs independently and is not cancelled. |
The tool had already completed; its output was discarded… |
monitor — signal pre-aborted |
Tool call cancelled before execution. |
same |
monitor — abort 1 macrotask / sync / within beforeToolLaunch |
Tool call cancelled before execution. |
same |
monitor — abort at 0 ms |
Tool call cancelled by user. |
same |
workflow (background) — pre-aborted / sync / microtask / beforeToolLaunch |
Tool call cancelled before execution. |
same |
ask_user_question — user declines the dialog |
User did not allow tool call |
same |
ask_user_question — turn aborted while the dialog is open |
awaiting_approval, no model text |
same |
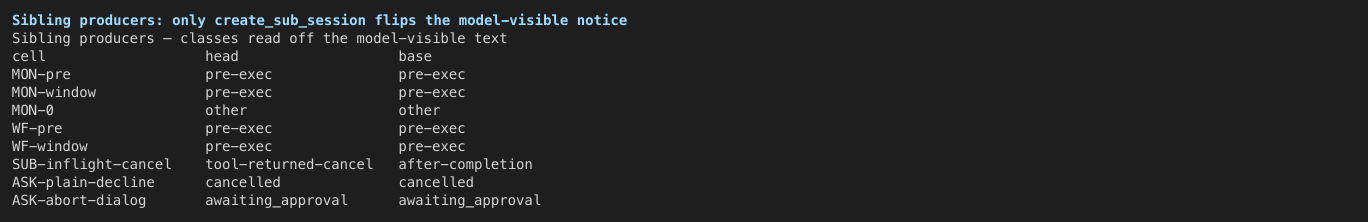
So exactly one of the four new markers changes what the model sees in a reachable flow.
Findings (non-blocking)
N1 — Suggestion: three of the four new markers are not observable in any path I could drive
monitor, workflow (background early abort) and ask_user_question set interruptedBeforeCompletion, but the scheduler cancels those calls before execute() runs, so the marker is never read and the model keeps the pre-existing pre-execution / user-denied wording. The commit message says "the scheduler's returned-means-finished read was wrong for each"; measured, only create_sub_session reaches that read.
This is not a defect — the markers are harmless defence if the pre-execution guard ever misses — but the claim should be bounded to the producer that is demonstrably reachable. Reproduce with harness/producers.mjs (cells MON-*, WF-*, ASK-*).
N2 — Suggestion: ask_user_question marks a plain decline as "interrupted"
execute() sets the marker whenever !wasAnswered, which includes the user simply declining the question (should return cancellation message when user declines pins exactly that). A decline is a completed decision, not interrupted work. It is inert today — the scheduler only reads the marker in its post-execute abort branch, and a decline takes the user-denied path — but a future read site would report a finished interaction as "do not retry". The code comment says "a plain decline leaves the scheduler on its normal path", which is true of the reader, not of the write.
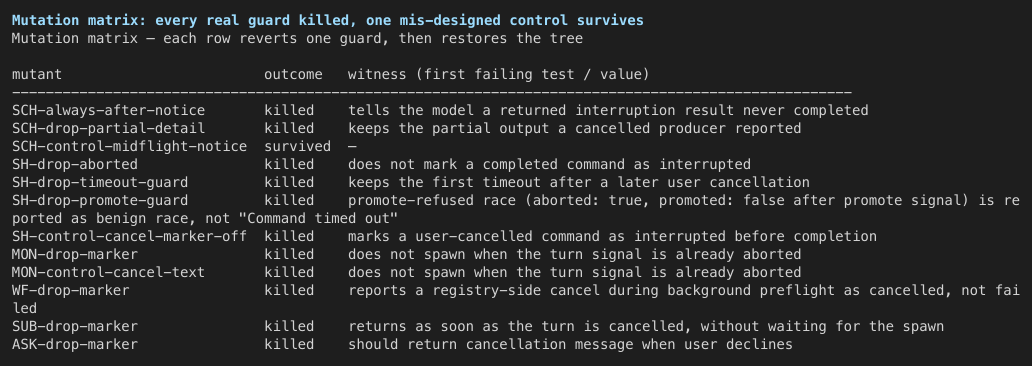
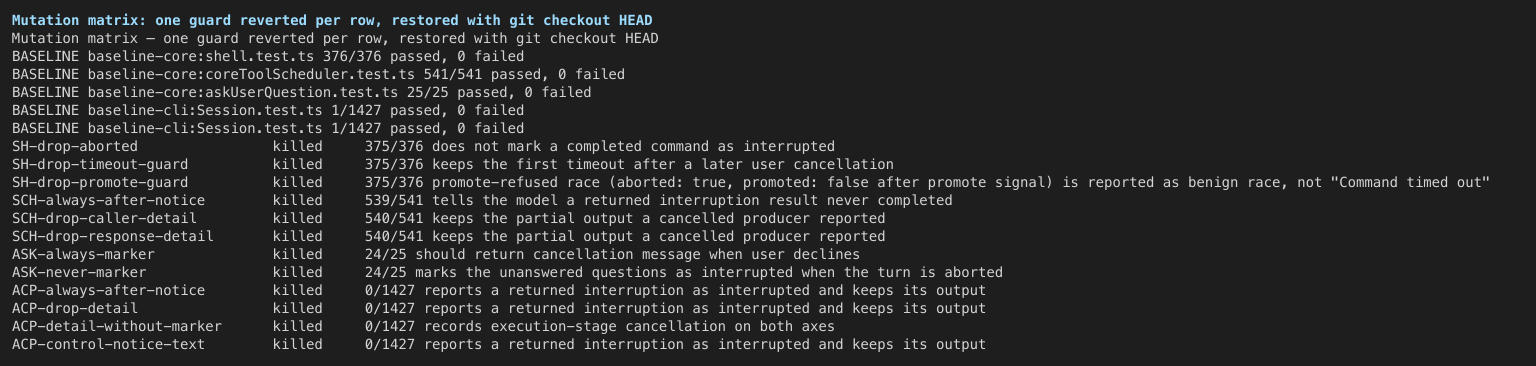
Mutation matrix
Every row reverts one guard in the head tree, runs the named suite, and restores the tree with git checkout HEAD --; the runner refuses a dirty tree or a non-unique anchor. Head baseline: 917/917 across coreToolScheduler.test.ts + shell.test.ts.
| Mutant | Outcome | Witness |
|---|---|---|
| scheduler: always pick the "already completed" notice | killed | author's returned-interruption case |
| scheduler: drop the appended detail | killed | keeps the partial output a cancelled producer reported |
shell: drop result.aborted |
killed | does not mark a completed command as interrupted |
shell: drop !wasTimeout |
killed | keeps the first timeout after a later user cancellation |
shell: drop !wasPromoteRefused |
killed | promote-refused race case |
| shell: marker on non-cancelled commands (positive control) | killed | marks a user-cancelled command as interrupted before completion |
| monitor: drop marker / change cancel text | killed / killed | does not spawn when the turn signal is already aborted |
| workflow: drop marker | killed (3 tests) | reports a registry-side cancel during background preflight as cancelled, not failed |
| create_sub_session: drop marker | killed | returns as soon as the turn is cancelled, without waiting for the spawn |
| ask_user_question: drop marker | killed | should return cancellation message when user declines |
| scheduler: flip the before-completion arm of the mid-flight test (mis-designed control) | survived | — |
The last row is excluded from the tally and is not a coverage claim: that test feeds a thrown AbortError, which never reads the mutated variable, so the mutation could not affect it. The genuine positive controls are the two rows that mutate the same files and are killed (SCH-always-after-notice, SH-control-cancel-marker-off).
Not covered
- Approval mode
default, full chain. Only a turn abort while the question dialog is open was driven (identical on both arms,awaiting_approval, no model text). The dialog → approve → running → cancel chain was not. - Container and SSH execution environments.
SshExecutionEnvironment.execute()rebuilds the result itself and never sets the marker — inferred from code, not measured. - Windows, and a real TUI Esc. Esc →
cancelOngoingRequest()→abort()is read from code, not driven through a terminal. - Workflow cancelled after its background start begins. My registry stub only implements
hasCompletionCallback/get/list, soreserveStartthrew; theWorkflowStartCancelledError→startCancelledResult()path was not driven. - Monitor with a real spawn.
getMonitorRegistrywas stubbed without a real registry; theMonitor failed to startcells are harness limits, not product behaviour. - PR CI. Checks were still pending when the round ran (several lanes already passed, but none were used as evidence).
- Per-commit attribution. The matrix is per-guard; the two production commits (
6e6600e,97b8a0b) were not mutated commit-by-commit.
Methodology
Two worktrees (head 46db90b6, base 1ccf0d43) installed with scripts/setup-worktree.js and built with npm run build --workspace=@qwen-code/qwen-code-core under Node 22.23.4; the @qwen-code/* realpath assertion confirms each tree resolves its own packages/core, and the head dist carries interruptedBeforeCompletion (3 + 1 occurrences) while the base dist carries none — the positive control for the build. Harnesses in harness/ (shell-ab.mjs, producers.mjs, mutate.mjs, ledger.mjs) import each arm's compiled dist and read the exact functionResponse payload. A trial merge into current main (10b48ab9, none of the PR's files touched since the base) is conflict-free and produces tree c9d8bbdc752f74f16e794850479bcd940ae9f218; the targeted gate is 917/917 on both the head tree and the merged tree. Raw logs are logs-ab-*.log, logs-producers-*.log, logs-mutate-*.log, logs-gate-*.log; assertions.json is generated from those logs by harness/ledger.mjs.
A plain decline is a completed decision. Setting the marker on it is inert
today, but would report a finished interaction as "do not retry" if a future
read site consumed it.
|
Thanks — both notes are addressed. N1 — the claim is now bounded, the markers stay. The description states that only N2 — fixed in
Head is |

|
Qwen Code review did not complete successfully. Qwen review exited with status 1. A transient error is retried automatically; if you are seeing this, retry with |

 doudouOUC
left a comment
doudouOUC
left a comment
There was a problem hiding this comment.
EN
Re-checked this at 5ddffc30, and the core of the change holds up: the new marker reuses the exact predicate that already derives returnDisplay.outcome in the shell tool, so the two classifications cannot drift; timeout, promote-refused, real-failure and normal-completion paths never set it and each has a witness assertion; the detail gate keeps the post-completion cancel discarding output as before. CI is green on this head too — the unit lane actually ran this time (Run tests and generate reports: success) and Check lint gate freshness passes, so the evidence gap from the earlier review round is closed.
Three things from reading the consumers of that result:
1. The ACP session pipeline still reports a cancelled shell as completed (the same bug, different pipeline). packages/cli/src/acp-integration/session/Session.ts:18923-18933 picks TOOL_POST_EXECUTION_CANCELLED_MESSAGE — the constant at :957, "The tool had already completed; its output was discarded." — whenever the turn signal is aborted after execute() returned. It computes the same predicate the scheduler does (:18574-18577), has toolResult in hand, and never reads interruptedBeforeCompletion, then replaces responseParts wholesale so the shell's "Below is the output before it was cancelled" text is dropped too. That file says of itself that it mirrors CoreToolScheduler, and Session.test.ts:50468-50470 currently pins the old string. The effect is that in every session driven through the ACP agent — the web shell, IDE/ACP clients, qwen --acp — a shell killed by Esc still reaches the model as finished, with its partial output lost. Risk & Scope names the managed-runtime wrapper as the remaining surface; this one is separate and reachable today. Either reading the flag at the same predicate (BEFORE message + the result's own text as the detail, exactly as the scheduler now does) or adding it to the out-of-scope list would settle it.
2. The sub-agent tool is still mislabelled, and it is worth saying so in the body. packages/core/src/tools/agent/agent.ts:5097-5130 returns its cancel as llmContent: [{ text: … }] carrying "Agent was cancelled by the user." plus "Partial result follows:", with no marker, so the scheduler still replaces it with the after-completion notice and the partial sub-agent result is lost. Your reply explains why it was left alone, and that reasoning is sound — but it cannot be fixed by setting the flag alone, because the new detail gate at coreToolScheduler.ts:6656-6659 requires a string llmContent and this producer returns parts. One line in Risk & Scope recording that the sub-agent tool is not covered (and why the flag alone would not be enough) would keep the "no model-visible change is claimed" contract intact for a reader who only reads the description.
3. One narrow race now reports a clean exit as interrupted — pre-existing, no action needed. finalizeResult() in packages/core/src/services/shellExecutionService.ts:2483-2490 resolves with aborted: abortSignal.aborted read after the settle/drain chain and the awaited render, so an Esc landing in that window flags a command that already exited 0 as aborted; the new marker then propagates it. The tool layer already said "cancelled" there before this PR, so this is not something to fix here — I mention it only because the description's "only a user cancel sets the marker" framing reads stronger than the code.
None of this is a regression, and the diff itself is careful. Item 1 is the one I would like a decision on: fix, or record as a follow-up surface the way the managed-runtime wrapper already is.
ZH
针对 5ddffc30 重新看了一遍,改动的核心成立:新标记复用了 shell 工具里推导 returnDisplay.outcome 的那同一个判定式,两处分类不可能漂移;超时、后台提升被拒、真实失败、正常完成这几条路径都不会打标记,且各自都有断言见证;detail 的条件门让"已完成后取消"仍然和以前一样丢弃输出。这个 head 上 CI 也是绿的——这次单元测试 lane 真的跑到了(Run tests and generate reports: success),Check lint gate freshness 也通过,上一轮评审提到的证据缺口已经补上。
读完消费这个结果的几条路径后,有三点:
1. ACP session 管线仍把被取消的 shell 报成已完成(同一个 bug,另一条管线)。 packages/cli/src/acp-integration/session/Session.ts:18923-18933 在 execute() 返回后只要回合信号被中断,就固定选 TOOL_POST_EXECUTION_CANCELLED_MESSAGE(常量在 :957,即"The tool had already completed; its output was discarded.")。它计算的判定式和调度器完全一样(:18574-18577),此时 toolResult 就在手上,却从不读 interruptedBeforeCompletion,随后整体替换 responseParts,于是 shell 自己那段"Below is the output before it was cancelled"也一起丢了。该文件自称是 CoreToolScheduler 的镜像实现,而 Session.test.ts:50468-50470 目前正好把这个旧字符串钉住了。后果是:所有通过 ACP agent 跑的会话——web shell、IDE/ACP 客户端、qwen --acp——里按 Esc 杀掉的 shell 仍然以"已完成"到达模型,并且丢掉部分输出。Risk & Scope 里只点了 managed-runtime 包装层是剩余 surface,这一条是另一条、且当下就可达。要么在同一判定式处读取该标记(BEFORE 消息 + 把结果自身文本作为 detail,与调度器现在的做法一致),要么把这条 surface 也写进 out-of-scope。
2. sub-agent 工具仍被误标,值得在正文里说明。 packages/core/src/tools/agent/agent.ts:5097-5130 的取消返回是 llmContent: [{ text: … }],内容是"Agent was cancelled by the user."加"Partial result follows:",没有打标记,因此调度器仍会用"已完成后取消"的消息替换它,sub-agent 的部分结果被丢弃。你在回复里解释了为什么先不动它,理由成立——但它光靠打标记也修不好,因为新增的 detail 条件门(coreToolScheduler.ts:6656-6659)要求 llmContent 是字符串,而这里的生产者返回的是 parts。在 Risk & Scope 里加一行,说明 sub-agent 工具未覆盖、以及为什么只打标记不够,能让只读描述的人继续相信"未声称模型可见行为有变化"这个契约。
3. 一个很窄的竞态现在会把正常退出报成被中断——既有问题,本 PR 无需处理。 packages/core/src/services/shellExecutionService.ts:2483-2490 的 finalizeResult() 在 settle/drain 链与 await 渲染之后才读 abortSignal.aborted 再 resolve,因此落在这个窗口里的 Esc 会把一条已经以 0 退出的命令标记为 aborted,新标记随后把它传播出去。这个问题在本 PR 之前工具层就已经说成"cancelled"了,所以不是这里要修的事——我提它只是因为描述里"只有用户取消才会打标记"的说法比代码实际更强。
以上都不是回归,diff 本身也很谨慎。第 1 条是我希望有个决定的地方:修掉,还是像 managed-runtime 包装层那样记为后续 surface。
|
Thanks — decisions on all three, at
The PR description now names the ACP path as covered and the sub-agent tool as out of scope. Focused runs: the two ACP cancellation cases, plus the existing scheduler/shell/question suites. |
|
Qwen Code review timed out. Qwen review timed out after 10800 seconds (of the 180-minute budget). For large PRs, retry with a longer timeout by commenting: |


 2SinceJuly
left a comment
2SinceJuly
left a comment
There was a problem hiding this comment.
All three are settled at the current head, which is now 5c008e68.
-
Fixed rather than deferred.
5c008e68 fix(cli): report an interrupted shell as interrupted in ACP sessionstakes your first option: the ACP pipeline readsinterruptedBeforeCompletionat the same predicate that already selects the BEFORE message, uses the result's own text as the detail, and no longer replacesresponsePartswholesale.Session.test.tspins the new string instead of the old one, so the web shell / IDE /qwen --acppath now reports an Esc'd shell as interrupted with its partial output intact. -
Recorded in Risk & Scope. The description now says the sub-agent tool is not covered, and why the flag alone would not be enough: it returns its cancel as content parts and the scheduler's detail gate requires a string
llmContent. -
No change, as you suggested. The
finalizeResult()race is pre-existing and the tool layer already said "cancelled" there before this PR; the description no longer claims otherwise.
Not run locally this round: the packages/cli suite. CI on the head that carries 5c008e68 is what I am relying on for the ACP change.
|
The failing Recent |
|
Verdict: 中文摘要(点击展开)结论:
Previous round's findings
What changed since round 2Round 2 verified
Everything else in Central claim and scheduler A/BClaim: a shell killed by a user cancel must reach the model as interrupted mid-work, with the output it produced before the kill. Both arms load their own compiled
Head 11/11; base 6/11 — the five cancel cells are expected red, every neighbouring outcome matches. Witness:
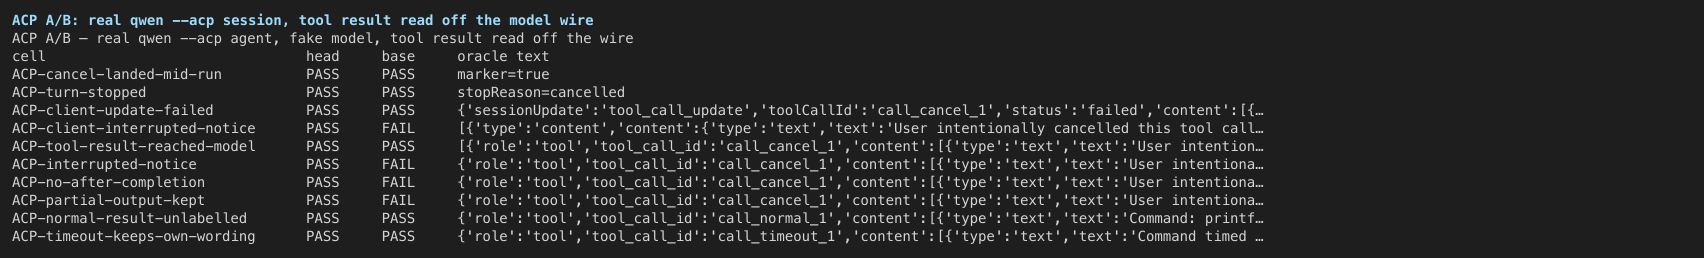
The ACP surface (new in this round)
Head 10/10; base 6/10 with the four flipped cells expected red. The same harness on the trial merge is 10/10. Witness:
The two model-wire payloads, verbatim: On base the terminal client update for the same call carries Sibling producers, re-measured
So N1 still stands exactly as the description now bounds it. Witness:
Mutation matrixEvery row reverts one guard, runs the named suite, and restores with
12/12 killed, each with a named witness. Witness:
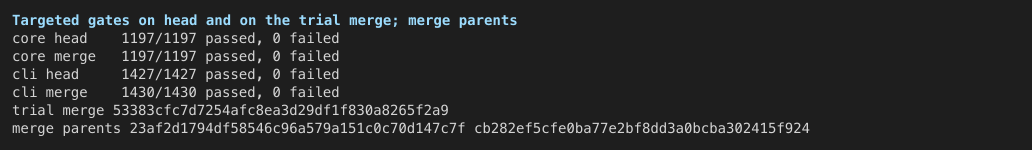
Targeted gates
The merge suite is three tests larger because
Findings (non-blocking)ACP reports the terminal client status as
|
|
No code change from this round. P1, P2 and N2 are confirmed fixed at the head you measured; P3 stays out of scope as declared in the PR body, and N1 stays bounded at On your CI note: the red checks on this head are |


 yiliang114
left a comment
yiliang114
left a comment
There was a problem hiding this comment.
APPROVE at c08d50a.
The change adds an interruptedBeforeCompletion marker to ToolResult and wires it through 5 producers (shell on user cancel, monitor, workflow, create-sub-session, askUserQuestion on abort) and 2 consumers (CoreToolScheduler + ACP Session). The predicate logic is correct at every site:
- shell: sets only on
aborted && !wasTimeout && !wasPromoteRefused— correct exclusion of timeouts and promote refusals. - askUserQuestion: sets only when the signal is aborted, not on a plain decline — correct distinction between interrupted and decided.
- scheduler: reads the marker to choose between the new
TOOL_CANCELLED_BEFORE_COMPLETION_MESSAGEand the existingTOOL_CANCELLED_AFTER_COMPLETION_MESSAGE, and appends partial output as detail — mirrors the old shape's output-preservation policy. - ACP Session: mirrors the scheduler's logic, including partial output forwarding.
Tests cover every producer's set/unset behavior and both consumers' message selection. The disclosed out-of-scope gaps (managed-runtime, sub-agent tool, confirmation dialog race) are documented in the PR body and are not regressions. No security, concurrency, or type-safety concerns.

|
Closeout (b) isn't met. This isn't purely internal: the diff adds a model-visible Separately, the head is still blocked on queued required CI ( |
|
Same situation as the gate describes, and the head has not moved: The What the change is supposed to be observable as, for whoever does have that environment: with the marker set, the scheduler's cancellation notice becomes "User intentionally cancelled this tool call. Stop and await further instructions; do not retry or work around it." instead of the completion notice, so the model should report the call as interrupted rather than finished. Agreed the queued required CI makes this moot this round. If you can tell me the marker's expected format, I will produce it from a real run as soon as one is available to me. |

 qwen-code-review-bot
left a comment
qwen-code-review-bot
left a comment
There was a problem hiding this comment.
Reviewed. Suggestions are inline.
Not explored to full depth (tool budget reached): "agent 6a": none — I finished the walk of every hunk and of both consumers..
— deepseek-v4.1-flash-1017 via Qwen Code /review (v0.26.9)
| const TOOL_CANCELLED_BEFORE_COMPLETION_MESSAGE = | ||
| 'User intentionally cancelled this tool call. Stop and await further instructions; do not retry or work around it.'; |
There was a problem hiding this comment.
[Suggestion] R1-1: This constant duplicates core's TOOL_CANCELLED_BEFORE_COMPLETION_MESSAGE by hand, and the sibling copy one line above has already drifted: core's after-completion notice ends with “…User intentionally cancelled. Stop and await further instructions; do not retry.” (the #10170 stop directive), while TOOL_POST_EXECUTION_CANCELLED_MESSAGE here stops at “…was discarded.” So every ACP-driven session — the web shell, IDE/ACP clients, qwen --acp — already gives the model a weaker cancellation instruction than the TUI, and a future edit to core's new wording will silently leave this copy stale in exactly the same way.
Witness:
CORE AFTER : "The tool had already completed; its output was discarded. User intentionally cancelled. Stop and await further instructions; do not retry."
ACP  AFTER : "The tool had already completed; its output was discarded."
AFTER equal? false
CORE BEFORE: "User intentionally cancelled this tool call. Stop and await further instructions; do not retry or work around it."
ACP  BEFORE: "User intentionally cancelled this tool call. Stop and await further instructions; do not retry or work around it."
BEFORE equal? true
Export both constants from packages/core/src/core/coreToolScheduler.ts and import them here, deleting both local copies — that also repairs the existing drift:
import {
  TOOL_CANCELLED_AFTER_COMPLETION_MESSAGE,
  TOOL_CANCELLED_BEFORE_COMPLETION_MESSAGE,
} from '@qwen-code/qwen-code-core/core/coreToolScheduler.js';
Session.ts is allowlisted for root-barrel core imports (eslint.legacy-core-barrel-imports.mjs:23), but new imports belong on the defining module @qwen-code/qwen-code-core/core/coreToolScheduler.js, per AGENTS.md's “Core imports in cli” rule.
— deepseek-v4.1-flash-1017 via Qwen Code /review (v0.26.9)
| ? new Error(toolResult.error.message) | ||
| : status === 'cancelled' | ||
| ? new Error(TOOL_POST_EXECUTION_CANCELLED_MESSAGE) | ||
| ? new Error(cancelReason) |
There was a problem hiding this comment.
[Suggestion] R1-2: This line feeds the client-visible tool error — responseError goes to this.toolCallEmitter.emitResult({ …, error: responseError }), which renders errorMessage: params.error?.message — but nothing in Session.test.ts pins it. The new case asserts only result.parts[0].functionResponse.response, and emitResult appears nowhere in the 65,996-line file. Revert this to new Error(TOOL_POST_EXECUTION_CANCELLED_MESSAGE) and the suite stays green while the model is told “User intentionally cancelled this tool call…” and the user's UI shows “The tool had already completed; its output was discarded.” — the two surfaces disagreeing about whether work landed is the defect this PR removes.
Witness:
witness: not run — the closest capability is a mutation probe (revert this line, rerun Session.test.ts); the scratch tree was unavailable and a mutation may not be applied in the shared worktree. Static sweep of the real file: 0 occurrences of `emitResult` in Session.test.ts, 4 of `errorMessage`, none on a cancellation path.
In the new test, spy on ToolCallEmitter.prototype.emitResult (sibling methods are already spied this way around Session.test.ts:50770) and assert the recorded error?.message is the before-completion notice plus the preserved llmContent.
The assertion must go red when this line is reverted to new Error(TOOL_POST_EXECUTION_CANCELLED_MESSAGE) — otherwise the client-visible half of the ACP fix is unprotected.
— deepseek-v4.1-flash-1017 via Qwen Code /review (v0.26.9)
| // The notice says the call did not finish; the producer's own text says how | ||
| // far it got. Replacing the whole payload with the notice loses the partial | ||
| // output the model needs to decide what remains. | ||
| it('keeps the partial output a cancelled producer reported', async () => { |
There was a problem hiding this comment.
[Suggestion] R1-3: The table above pins the positive half of the new detail guard but not the negative half. The post-completion row (textResult('done'), no marker) asserts only that the after-completion notice is present and the before-completion notice absent — never that done is absent. Drop toolResult.interruptedBeforeCompletion from the detail ternary at coreToolScheduler.ts:6656-6658 and that row still passes, while a completed command's output is re-appended to a body that says “The tool had already completed; its output was discarded.” The ACP side is guarded against the mirror mutation by the exact-equality test at Session.test.ts:52748; the scheduler side has no equivalent.
Witness:
witness: not run — the closest capability is `revert-hunk` on coreToolScheduler.ts:6655-6659 plus a rerun of the two scheduler cases; the scratch tree was unavailable. Sweep of the real assertion set: 0 hits of `not.toContain('done')` in the 15,837-line file; the asserted pair is only toContain('The tool had already completed') / not.toContain('User intentionally cancelled this tool call. Stop'), which a leaked "done" does not violate.
| it('keeps the partial output a cancelled producer reported', async () => { | |
| expect(responseText).toContain(notice); | |
| expect(responseText).not.toContain(wrongNotice); | |
| expect(responseText).not.toContain('done'); |
The absence assertion must go red when toolResult.interruptedBeforeCompletion is removed from the detail ternary — that is the mutation it exists to catch.
— deepseek-v4.1-flash-1017 via Qwen Code /review (v0.26.9)
| ...(result.aborted && !wasTimeout && !wasPromoteRefused | ||
| ? { interruptedBeforeCompletion: true } | ||
| : {}), |
There was a problem hiding this comment.
[Suggestion] R1-4: The marker is attached only at this foreground result builder, so other returned-cancel arms still produce the notice this PR removes. sedEditCancelledResult()'s user-cancel arm (shell.ts:2006-2009) returns { llmContent: 'Command was cancelled by user before it could complete.', returnDisplay: 'Command cancelled by user.' } with no marker, and it is reached whenever Esc lands while a prepared simulated sed -i awaits waitForSedOperation (shell.ts:2062-2068, 2116-2126) — an edit that never reached writeTextFile. The scheduler then sees aborted with the marker undefined, selects TOOL_CANCELLED_AFTER_COMPLETION_MESSAGE, passes no detail, and the model is told the edit already completed, so it may act as if the file changed. exitPlanMode.ts:268 and :343 are the same shape (a plain noActionResult on signal.aborted). Neither arm is in the PR body's out-of-scope list, and both are exactly the “returned rather than thrown” class this marker exists for.
Witness:
npx vitest run src/tools/shell.test.ts -t "sed execution is cancelled after reading"
 → 1 passed  (confirms the sed cancel is a returned ToolResult, whose literal at shell.ts:2006-2013 carries only llmContent/returnDisplay)

npx vitest run src/core/coreToolScheduler.test.ts -t "tells the model a post-completion cancellation discarded finished work"
 → 1 passed  (that row asserts the model sees "The tool had already completed" for a marker-less returned result — the outcome this arm produces)
// sedEditCancelledResult(), non-timeout arm
return {
  llmContent: 'Command was cancelled by user before it could complete.',
  returnDisplay: 'Command cancelled by user.',
  interruptedBeforeCompletion: true,
};
The TimeoutError arm of the same helper (shell.ts:1993-2003) returns error.type = ToolErrorType.EXECUTION_TIMEOUT and must stay unflagged — the scheduler derives isTimeout from exactly that type, and shell.test.ts:5356-5360 pins expect(result.interruptedBeforeCompletion).toBeUndefined() for the timed-out path; exitPlanMode's neighbouring returns at :263, :277 and :352 are completed no-ops and must not be marked either, so the marker belongs on the returns rather than in the shared helper.
A simulated sed edit test that aborts while trackEdit is pending (asserting result.interruptedBeforeCompletion === true) and an exitPlanMode test that aborts during requestPlanApproval must both go red without the added field.
— deepseek-v4.1-flash-1017 via Qwen Code /review (v0.26.9)
| // Same returned-interruption shape as the monitor: nothing ran, so the | ||
| // scheduler must not tell the model the call completed. | ||
| interruptedBeforeCompletion: true, |
There was a problem hiding this comment.
[Suggestion] R1-5: WorkflowStartCancelledError is raised for a registry-side cancel (cancelStarting/abortAll) that aborts the run's controller “while the caller's signal stays live, in either mode” (workflow.ts:566-580). This marker is set on that path too, but both consumers read it only inside an aborted-signal branch (coreToolScheduler.ts:6609, Session.ts:19654), and aborted = parentAbortedAtExecutionSettle && !isTimeout is false there — so the call settles success, fires a PostToolUse success hook and is recorded as completed while its own text says it was cancelled, and the marker this diff adds contributes nothing. That contradicts the field's doc comment (“The scheduler uses it to tell the model the call was interrupted rather than completed”) and the PR body's statement that these defensive producers are cancelled before execute() runs.
Witness:
npx vitest run src/tools/workflow/workflow.test.ts -t "registry-side cancel"
 Tests 2 passed | 146 skipped (148)

workflow.test.ts:1092-1113 asserts expect(caller.signal.aborted).toBe(false)
beside the now-marked CANCELLED_BEFORE_START. Read-site sweep: the marker has
exactly 3 read expressions package-wide, all inside a signal.aborted branch.
Either document the coupling the field actually has — “only honoured when the turn signal is aborted” — or widen the two read sites so a marked result settles cancelled regardless of the caller signal. Do not simply drop the field from startCancelledResult(): the background early return (workflow.ts:546) and the background catch arm (:583-588) do abort the caller signal, and there the marker is read and correct.
const aborted = parentAbortedAtExecutionSettle && !isTimeout; (coreToolScheduler.ts:6564-6565) keeps a structured EXECUTION_TIMEOUT out of the cancel path, so any fix that lets the marker alone force cancelled must not reclassify a timeout.
If you widen the read sites instead of documenting, a scheduler test whose execute() resolves a marked result with a live signal must assert the call settles cancelled — today it settles success.
— deepseek-v4.1-flash-1017 via Qwen Code /review (v0.26.9)
…n-hook

main advanced 11 commits (stacked-skill overflow #16404, workflow agent
approvals #16432, daemon UI tool blocks #16306, sibling model settings
#15829, late snapshot publication claim #16489, inline FQN imports in
runtime modules #16504, cancelled shell as interrupted #15836, CSI statement
helper fold #16503, Maven suite cache write-back #15274, sed char match
#15701, Ink TUI tool-batch round #16428). One conflict, the workflow size
ratchet:

- .size-baseline: sdk-java.yml auto-merged to 167124 bytes (HEAD recorded
  161927 / main 165241, both below the combined actual), so record the actual
  merged size 167124 per the ratchet's "record the real size in the same PR"
  rule. The absolute gate (470000) and the 4096-byte baseline allowance both
  pass.

No source conflict: main's commits did not touch this branch's A3 source
files, so RuntimeBrokerService / RuntimeExecutionRecovery (R18-1/R19-1
observe-only mount-handback guard) and the cli serve fence are unchanged.

Verification: check-workflow-size.sh green (bash5); workflow meta tests
(workflow-size + sdk-java-workflow + hosted-process-ci) 428 green; workspace
build and ClassSizeRatchetTest re-run after the merge.
|
Released in v0.27.0. |


What this PR does
Adds an explicit
interruptedBeforeCompletionmarker to a tool result and sets it when the shell tool is cancelled by the user. The scheduler's post-execute cancellation branch now chooses the cancellation notice from that marker instead of assuming that a returned result means the tool finished. The ACP session pipeline, which mirrors that branch forqwen --acp, the web shell and IDE clients, reads the same marker and keeps the producer's partial output as the detail.Why it's needed
On Esc/Ctrl+C the shell tool kills the process group but returns an ordinary result whose own content already says the command was cancelled. The scheduler's
abortedbranch hardcoded "The tool had already completed; its output was discarded", which discards that truthful text and tells the model the work finished — and not to retry it. For half-run migrations or deploys, a step that was killed is recorded as done.The shell tool is not the only possible producer of this shape: any tool that reports interruption by returning rather than throwing was mislabelled the same way, so the signal lives on the result rather than being inferred from shell's wording. Of the producers that now set it, only
create_sub_sessionwas shown reachable in measurement.monitor,workflow(early abort) andask_user_questionset it as defence: the scheduler cancels those calls beforeexecute()runs, so the marker is not read on those paths today.ask_user_questionsets it only when the turn was actually aborted — a plain decline is a completed decision and leaves the marker unset.Reviewer Test Plan
How to verify
work.shwritingstart, sleeping, thendone), run it through the CLI and press Esc about 1s in.Before: the tool result says the tool had already completed and that the output was discarded. After: it says the call was intentionally cancelled and that it must not retry or work around it.
Timeouts and background-promote refusals keep their existing outcomes; only a user cancel sets the marker on the shell path.
Evidence (Before & After)
Non-UI change, so N/A for screenshots. The new scheduler table case fails on the previous code with
The tool had already completed; its output was discardedand passes here; the shell test asserts the marker is set only on a user cancel; the question-tool tests assert it is set only when the turn was aborted; and the new ACP case asserts an interrupted result reaches the model as interrupted, with its partial output appended, while the unflagged case keeps the old wording.Tested on
Unit tests on macOS and in a
node:22-bookwormcontainer; Windows not exercised.Environment (optional)
cd packages/core && npx vitest run src/core/coreToolScheduler.test.ts src/tools/shell.test.ts src/tools/askUserQuestion.test.ts(942 tests);cd packages/cli && npx vitest run src/acp-integration/session/Session.test.ts.Risk & Scope
create_sub_sessionwas reachable in measurement), and read only by the cancelled branch.monitor,workflow(early abort) andask_user_questionset the marker defensively; the scheduler cancels them before execution, so no model-visible change is claimed for those paths. A call cancelled before it starts ("cancelled before it could start") is not covered. A cancel that lands while the shell's confirmation dialog is still open (approval modedefault) is also uncovered: it reports the generic cancelled reason, identically before and after this change. The managed-runtime surface still reports the old wording — its wrapper rebuilds a tool result from an explicit field whitelist that does not forward this marker — so this PR does not reach sessions whose tools run through that wrapper. Tracked as a follow-up rather than treated as fixed here. The sub-agent tool is also not covered: it returns its cancel as content parts and sets no marker, and the scheduler's detail gate requires a stringllmContent, so setting the marker alone would not preserve its partial result. The ACP pipeline is covered by this PR.Linked Issues
Closes #15833
Thanks @stars-spark for the detailed reproduction.